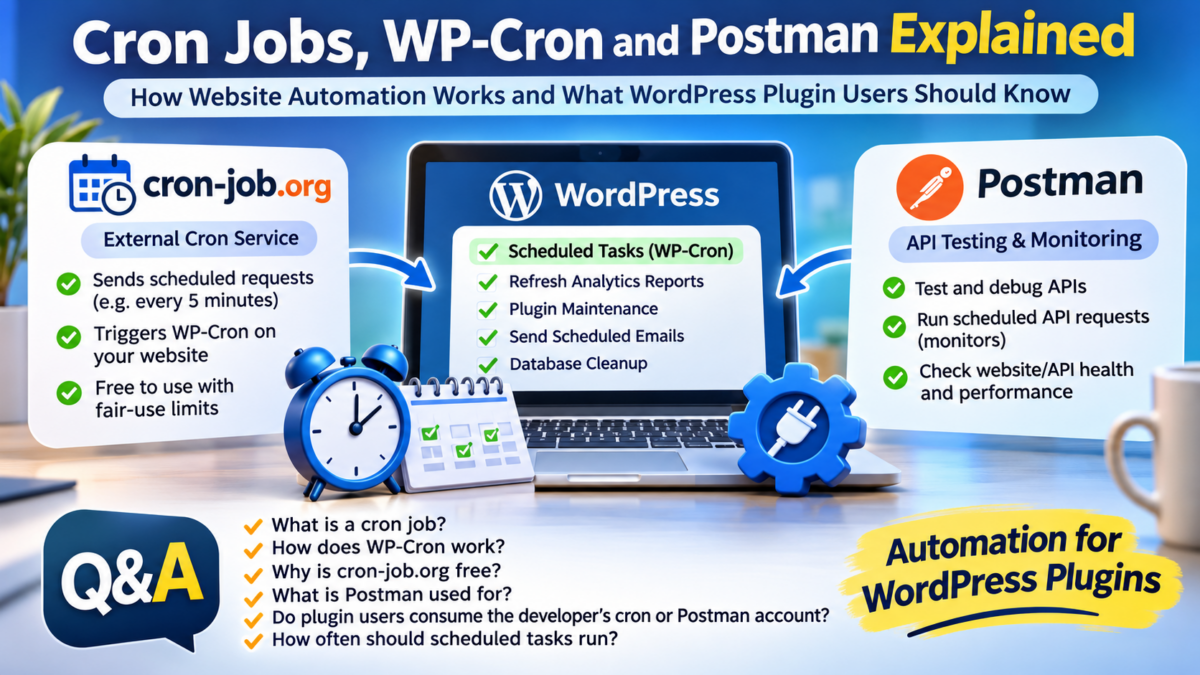
Cron Jobs, WordPress and Postman Explained: Are Free Automation Services Really Free?

Understanding how scheduled tasks work, why services such as cron-job.org offer free scheduling, and whether third-party WordPress plugin users consume the developer’s resources.

Automation has become an essential part of modern websites. WordPress plugins routinely perform background activities such as refreshing analytics, generating reports, checking website status, processing transactions and maintaining databases.

Many of these operations happen automatically, without requiring an administrator to log in and initiate them.

But how do websites perform these tasks? What exactly are cron jobs? Why do services such as cron-job.org offer free scheduling? And when someone downloads a WordPress plugin, does that person consume the developer’s external automation resources?

These questions are particularly relevant to WordPress developers who distribute plugins to other website owners.

Let’s explore the subject through a series of questions and answers.


1. What exactly is a cron job?

A cron job is an automated task scheduled to execute at a particular time or at recurring intervals.

The concept originated in Unix-like operating systems, where the cron utility manages scheduled commands.

For example, a server administrator might schedule a task to:

  • Back up a database every night.
  • Delete temporary files every week.
  • Generate a report every morning.
  • Check whether a website is responding.
  • Refresh information from an external API.

Instead of requiring someone to perform these activities manually, the scheduling system initiates them automatically.

A simple example would be scheduling a task to execute every five minutes.

This means that the task is scheduled to run 12 times every hour, or 288 times per day.

Cron jobs are therefore particularly useful for websites and applications that depend on regular background processing.

2. What is WordPress WP-Cron?

WordPress has its own scheduling mechanism called WP-Cron.

It allows WordPress itself and installed plugins to register scheduled tasks.

For example, a WordPress plugin might need to generate an analytics report every week. Rather than requiring the website administrator to generate the report manually, the plugin can register a recurring event with WP-Cron.

WordPress then attempts to execute that event when its scheduling mechanism is triggered.

Common examples include:

  • Publishing scheduled posts.
  • Checking for plugin updates.
  • Cleaning expired database records.
  • Sending scheduled emails.
  • Refreshing analytics reports.
  • Performing routine plugin maintenance.

An important distinction is that WP-Cron is not necessarily a continuously running background service.

By default, WordPress checks for scheduled tasks when the website receives visits. If a website receives very little traffic, a scheduled task might not execute exactly when expected.

This is one reason website administrators sometimes use an external cron service.

Official documentation: WordPress Cron – Plugin Developer Handbook

3. What is cron-job.org, and why is it free?

cron-job.org is an online scheduling service that allows website owners to configure recurring HTTP requests.

It essentially works like an automated alarm clock.

Instead of running a scheduled command directly on the website’s hosting server, the service periodically sends a request to a specified URL.

For example:

https://example.com/wp-cron.php?doing_wp_cron=1

When this URL is accessed, WordPress gets an opportunity to process its scheduled events.

A website owner can configure the external service to send this request every five minutes.

Why does cron-job.org offer this service for free?

According to its official FAQ, cron-job.org provides its service free of charge. It supports recurring requests, including schedules as frequent as once per minute.

The service operates its own infrastructure to schedule and send requests. Its business model and operating arrangements allow it to offer a free scheduling service.

However, free does not mean that the underlying infrastructure consumes no resources.

The service must maintain servers, scheduling systems, network connectivity and operational infrastructure.

The distinction is that the user does not have to operate that infrastructure independently.

Official resources:

4. Does a request every five minutes consume server resources?

Yes.

Every external request sent to a website requires some processing.

Consider a website configured to receive an external cron request every five minutes.

IntervalNumber of requests
Every hour12
Every day288
30 days8,640
365 days105,120

These figures demonstrate that even a seemingly small recurring request can generate a substantial number of requests over time.

However, the actual resource consumption depends on what happens after the request reaches the website.

For example, a request that simply triggers WordPress to check its scheduled events may be relatively lightweight.

A request that initiates database-intensive processing, generates reports or communicates with multiple external APIs can consume considerably more resources.

Therefore, the frequency of requests alone does not determine the overall server workload.

The nature of the scheduled operation is equally important.

5. What is Postman? Is it another cron service?

Postman is primarily a platform for developing, testing and monitoring APIs.

It is widely used by developers to examine how applications communicate with one another.

For example, a developer might use Postman to test whether an API:

  • Returns the expected response.
  • Accepts the correct authentication credentials.
  • Responds with the appropriate HTTP status code.
  • Returns valid JSON data.
  • Responds within an acceptable time.

Postman also provides monitoring and scheduled collection execution capabilities.

These features can periodically execute API requests and help developers identify problems.

However, Postman and cron-job.org serve different purposes.

Featurecron-job.orgPostman
Primary purposeSchedule recurring HTTP requestsDevelop, test and monitor APIs
Scheduled executionYesYes
Website maintenanceCan trigger WP-CronNot its primary purpose
API testingBasic HTTP request capabilityMajor functionality
External monitoringThrough recurring requestsThrough API monitors
Account-based usage limitsDepends on service policiesDepends on Postman plan

Postman is not a mandatory component of ordinary WordPress plugin scheduling.

Its scheduled features are optional developer and monitoring tools.

Official resources:

6. Does installing a WordPress plugin automatically connect it to the developer’s cron-job.org account?

No.

This is perhaps the most important distinction for WordPress plugin users and developers.

A typical WordPress plugin uses the scheduling infrastructure of the WordPress installation on which it is installed.

Consider an example.

A developer creates an analytics plugin that registers a scheduled event to refresh website statistics every day.

When another website owner installs that plugin:

  1. The plugin registers its scheduled event with that website’s WordPress installation.
  2. WordPress maintains the scheduled event.
  3. WordPress attempts to execute it through its own WP-Cron mechanism.
  4. The plugin performs the required operation on that website.

The developer’s personal cron-job.org account is not automatically involved.

The plugin does not need to use the developer’s external scheduling account simply because it was downloaded from the developer’s GitHub repository or WordPress plugin directory.

An example involving multiple websites

Suppose a developer publishes an analytics plugin used by 100 website owners.

Each website has its own WordPress installation.

The arrangement looks like this:

WebsiteScheduling mechanism
Website AIts own WP-Cron
Website BIts own WP-Cron
Website CIts own WP-Cron
Website DIts own WP-Cron
Website 100Its own WP-Cron

Each website independently executes its scheduled plugin tasks.

The developer does not automatically become responsible for running 100 websites’ scheduled operations.

7. Can plugin users consume the developer’s external API or automation resources?

There is an important exception.

Although ordinary WP-Cron scheduling is independent, a plugin can be programmed to communicate with external services using the developer’s own credentials or infrastructure.

For example, imagine a developer creates a plugin that sends every user’s analytics information to an API hosted on the developer’s server.

In that situation, every installation could generate requests against the developer’s infrastructure.

Similarly, if the plugin contains a shared API key belonging to the developer, users might indirectly consume the developer’s API quota.

The distinction is therefore not simply whether a plugin uses cron jobs.

It is whether the plugin relies on external services belonging to the developer.

Some examples:

Plugin operationResource generally consumed
WordPress scheduled database cleanupWebsite owner’s hosting
WordPress scheduled analytics refreshWebsite owner’s hosting and relevant API quota
External cron request configured by the website ownerWebsite owner’s external cron account
API request using the user’s own API keyUser’s API allocation
API request using the developer’s shared API keyDeveloper’s API allocation
Request to the developer’s central serverDeveloper’s server resources

This is an important architectural consideration when distributing free WordPress plugins.

8. Why do some plugins work without external cron configuration?

Because WP-Cron is already part of WordPress.

A plugin developer can register scheduled events without requiring the website owner to create an external account.

For example, a plugin might schedule a daily task using WordPress’s scheduling functions.

The plugin can work automatically after installation, provided the website’s WordPress scheduling mechanism is functioning.

An external cron service is generally an enhancement rather than a compulsory requirement.

It becomes particularly useful when:

  • A website receives very little traffic.
  • Scheduled tasks must execute more reliably.
  • Time-sensitive background operations are involved.
  • A plugin performs important periodic maintenance.
  • The website administrator wants more predictable scheduling.

For a small website with occasional background tasks, the default WordPress scheduling mechanism may be sufficient.

9. Is running an external cron service every five minutes excessive?

Not necessarily.

The appropriate frequency depends on the purpose of the scheduled operation.

For example:

TaskPossible scheduling frequency
Basic website maintenanceHourly or daily
Analytics report generationDaily or weekly
Transaction maintenanceDepending on transaction activity
Time-sensitive queue processingEvery few minutes
Website availability monitoringEvery few minutes
Database cleanupDaily or weekly

These are illustrative intervals, not universal recommendations.

A five-minute interval may be appropriate for a website that needs regular queue processing. It may be unnecessary for a plugin that generates a report only once a week.

The best approach is to schedule tasks according to their actual requirements rather than running everything as frequently as possible.

10. What should WordPress plugin developers consider when distributing free plugins?

Plugin developers should design their products so that each installation operates independently wherever practical.

A good architecture should consider the following:

1. Independent scheduling

Each WordPress installation should register and execute its own scheduled events.

2. Optional external cron

External cron services should be optional unless the plugin has a specific technical requirement.

3. User-owned API credentials

Where practical, users should provide their own API keys rather than relying on a developer’s shared credentials.

4. Efficient background processing

Scheduled tasks should avoid unnecessary database queries, repeated API requests and resource-intensive operations.

5. Retry management

Failed API requests should not trigger unlimited retries. Temporary failures should be handled with appropriate retry intervals.

6. Monitoring and diagnostics

Administrators should be able to see whether scheduled tasks are registered, when they last ran and whether they encountered errors.

7. Clear documentation

Plugin documentation should explain which operations happen locally, which require external services and which consume third-party API quotas.

These practices help developers distribute plugins without inadvertently creating an unsustainable infrastructure burden.


Conclusion: Free Automation Does Not Mean Resource-Free Automation

Cron jobs, WP-Cron and Postman help automate activities that would otherwise require manual intervention.

Although services such as cron-job.org provide free scheduling facilities, the requests they generate still consume resources on the destination server.

The key distinction is the location of those resources.

A typical WordPress plugin uses the scheduling infrastructure of the website on which it is installed. Installing a plugin does not automatically connect the installation to the developer’s personal cron-job.org or Postman account.

However, developers must pay attention to shared API keys, central servers and external services embedded in their plugins. These can create dependencies and usage costs across multiple installations.

Ultimately, good plugin architecture should make each installation as independent as possible.

The broader principle is simple: a plugin should generally use the website owner’s resources for its own background operations, rather than silently depending on the developer’s personal automation accounts or infrastructure.

That distinction is important not only for developers distributing free WordPress plugins, but also for website owners who want to understand what happens behind the scenes when they install an automated application.
Understanding the WordPress Technology Stack: Programming Language, Database, CMS and Web Server

WordPress is one of the world’s most widely used Content Management Systems (CMS). It enables individuals, businesses, bloggers, and developers to create and manage websites without having to develop every feature from scratch.

However, WordPress does not operate independently. It relies on several underlying technologies that work together to make a website functional.

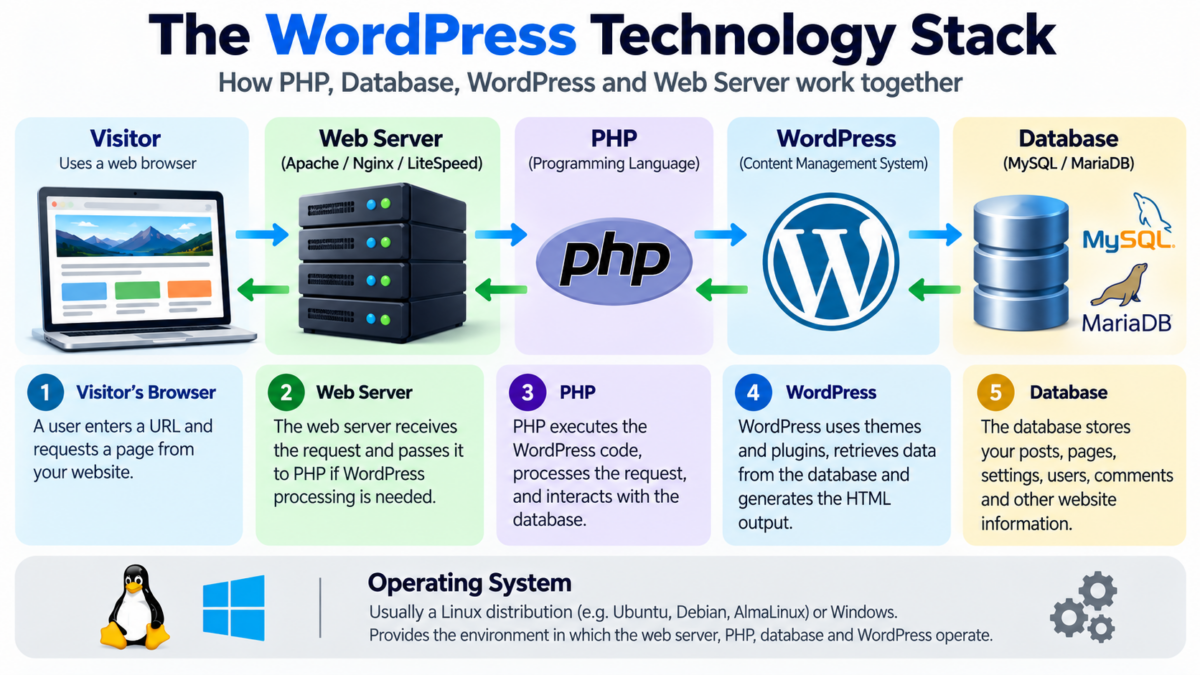
To understand how WordPress works, it is useful to classify its technology stack into four fundamental components:

  1. Programming Language
  2. Database Management System
  3. Content Management System (CMS)
  4. Web Server

An operating system provides the underlying environment in which these technologies operate.

Let’s examine each component, understand its responsibilities, and see how they combine to power a WordPress website.

1. Programming Language: PHP

A programming language provides instructions that a computer can execute to perform specific tasks.

WordPress is primarily developed using PHP, a server-side programming language.

PHP is responsible for executing the instructions that make WordPress function. It processes requests, communicates with databases, executes application logic, and generates dynamic webpage content.

What does PHP do in WordPress?

Consider a visitor opening a blog post on a WordPress website.

PHP helps WordPress:

  • Identify which webpage the visitor has requested.
  • Retrieve the relevant information from the database.
  • Process theme and plugin functionality.
  • Apply website settings and user permissions.
  • Generate the HTML output that the visitor’s browser receives.

PHP also powers the WordPress administration dashboard, enabling website owners to create posts, install plugins, change settings, and manage their websites.

Does PHP run on the visitor’s computer?

No. PHP normally runs on the server hosting the website.

The visitor’s browser receives the resulting HTML, CSS, JavaScript, images, and other frontend resources rather than executing the website’s PHP code.

This is why PHP is classified as a server-side programming language.

Other examples of server-side programming languages used in web development include Python, Java, Ruby, and JavaScript through Node.js.

However, WordPress itself primarily relies on PHP.

2. Database Management System: MySQL or MariaDB

Every dynamic website needs a mechanism to store and retrieve information.

WordPress uses a relational database management system (RDBMS) to manage its website data.

The two commonly used database systems for WordPress are:

  • MySQL
  • MariaDB

Although they are separate database management systems, MariaDB originated as a fork of MySQL and maintains substantial compatibility with it.

What is the role of a database?

A database stores information in an organised manner so that applications can retrieve, update, and manage it when required.

A typical WordPress database stores:

  • Blog posts and pages.
  • User accounts and password hashes.
  • Categories and tags.
  • Comments.
  • Website settings.
  • Plugin settings and data.
  • Navigation menu information.
  • Other structured website information.

WordPress organises much of this information into database tables.

For example:

Database tablePurpose
wp_postsStores posts, pages, and other content types
wp_usersStores user account information
wp_commentsStores comments
wp_optionsStores website settings
wp_termsStores categories, tags, and taxonomy terms
wp_postmetaStores additional information associated with posts

The prefix wp_ is the default and can be changed during installation.

Can WordPress use databases other than MySQL?

WordPress is designed around a database abstraction layer and has historically supported MySQL and MariaDB as its standard database backends.

Other database technologies exist, including PostgreSQL, SQLite, and Microsoft SQL Server. However, they are not interchangeable with the standard WordPress database setup. Using them generally requires additional compatibility layers or specialised implementations.

Therefore, when selecting a conventional WordPress hosting plan, MySQL or MariaDB compatibility is essential.

3. Content Management System: WordPress

The third component is the Content Management System itself.

WordPress is open-source software distributed through WordPress.org. It is primarily written in PHP and uses a database to store and retrieve website information.

While PHP provides the programming foundation and MySQL or MariaDB manages the data, WordPress brings these capabilities together into a practical website management platform.

What does WordPress provide?

WordPress provides several important features.

A. Administration Dashboard

The dashboard allows website owners to manage posts, pages, media, comments, users, settings, and other website functionality.

B. Themes

Themes control the visual presentation of a website.

They determine elements such as:

  • Page layouts.
  • Typography.
  • Colours.
  • Header and footer designs.
  • Templates.
  • Responsive presentation.

C. Plugins

Plugins extend the functionality of WordPress.

For example, plugins can add:

  • Contact forms.
  • SEO functionality.
  • Analytics dashboards.
  • Auction systems.
  • E-commerce facilities.
  • Mathematical calculators.
  • Membership systems.
  • Security features.

D. Content Management

WordPress enables website owners to create, edit, organise, publish, and update content through its administration interface.

E. User Management

WordPress provides different user roles and capabilities, allowing administrators to control who can access particular areas of a website.

WordPress.org versus WordPress.com

It is also important to understand the difference between WordPress.org and WordPress.com.

WordPress.org distributes the open-source WordPress software. Website owners can download it and install it on compatible hosting services.

This provides substantial control over hosting, themes, plugins, website files, and database management.

WordPress.com, on the other hand, is a hosted website platform operated by Automattic. It provides hosting and WordPress-based website management, with features and restrictions depending on the selected plan.

In simple terms:

  • WordPress.org provides the software.
  • WordPress.com provides a hosted website service based on WordPress.

4. Web Server: Apache, Nginx or LiteSpeed

A web server is another fundamental component of a WordPress hosting environment.

Its primary responsibility is to receive HTTP or HTTPS requests from visitors’ browsers and deliver the appropriate website resources and responses.

Common web server technologies include:

  • Apache.
  • Nginx.
  • LiteSpeed.

What does a web server do?

Suppose someone visits:

https://example.com/about-us

The browser sends a request to the server hosting the website.

The web server receives this request and determines how to handle it.

If the request requires WordPress processing, the web server passes it to PHP through an appropriate PHP handler, such as PHP-FPM.

PHP then executes the WordPress application, which may communicate with the database to retrieve the required information.

After processing, the generated response is returned through the web server to the visitor’s browser.

Web servers also deliver static resources such as:

  • Images.
  • CSS files.
  • JavaScript files.
  • Fonts.
  • Other downloadable resources.

The web server therefore acts as an important intermediary between website visitors and the server-side application.

5. The Operating System: The Underlying Environment

Although the four components discussed above form the main functional categories of the WordPress technology stack, an operating system provides the environment in which the hosting software operates.

Many WordPress hosting providers use Linux-based operating systems.

Examples include Ubuntu, Debian, and AlmaLinux.

The operating system manages system resources and provides the environment required to run PHP, database software, web servers, and other services.

However, WordPress is not restricted to Linux. It can also operate in compatible Windows-based hosting environments.

6. Frontend Technologies: HTML, CSS and JavaScript

The technologies discussed so far primarily explain how WordPress operates on the server.

However, a website also needs to present information to visitors in a browser.

Three important frontend technologies are HTML, CSS, and JavaScript.

HTML: Structure

HTML (HyperText Markup Language) defines the structure of webpages.

It describes elements such as:

  • Headings.
  • Paragraphs.
  • Images.
  • Links.
  • Lists.
  • Tables.

CSS: Presentation

CSS (Cascading Style Sheets) controls the visual appearance of webpages.

It defines:

  • Colours.
  • Fonts.
  • Spacing.
  • Page layouts.
  • Responsive designs.
  • Other visual properties.

JavaScript: Interactivity

JavaScript adds interactive functionality to webpages.

For example, it can power:

  • Dropdown menus.
  • Interactive calculators.
  • Form validation.
  • Dynamic content updates.
  • Interactive charts.
  • Other browser-side features.

These frontend technologies work alongside PHP and WordPress to deliver the website experience.

7. How Do These Components Work Together?

Let’s understand the complete process through a practical example.

Suppose a visitor opens a blog post on a WordPress website.

What happens behind the scenes?

Step 1: The visitor makes a request

The visitor enters a URL into a browser.

The browser sends an HTTP or HTTPS request to the web server hosting the website.

Step 2: The web server receives the request

The web server identifies the requested resource.

If the request requires WordPress processing, it passes the request to PHP.

Step 3: PHP executes WordPress

PHP executes the relevant WordPress code.

WordPress identifies the requested page or post and determines which theme templates, plugins, and application functions are required.

Step 4: WordPress communicates with the database

Through PHP, WordPress requests the necessary information from MySQL or MariaDB.

For example, it may request the post title, content, metadata, and other relevant information.

Step 5: The database returns the information

The database retrieves the requested information and sends it back to WordPress.

Step 6: WordPress generates the webpage

WordPress combines the retrieved information with the active theme, plugin functionality, and other relevant resources.

PHP executes the necessary instructions to generate the HTML response.

Step 7: The web server delivers the response

The web server sends the generated response to the visitor’s browser.

The browser processes the HTML, CSS, and JavaScript and displays the webpage.

This entire process generally takes place within a fraction of a second, although the actual time depends on hosting resources, database performance, caching, network conditions, and website complexity.

8. A Summary of the WordPress Technology Stack

The following table summarises the main components and their respective responsibilities.

ComponentTechnology examplesMain responsibility
Programming LanguagePHPExecutes application logic
Database Management SystemMySQL, MariaDBStores and retrieves information
Content Management SystemWordPressProvides website management and functionality
Web ServerApache, Nginx, LiteSpeedHandles requests and delivers responses
Operating SystemLinux, WindowsProvides the underlying operating environment
Frontend TechnologiesHTML, CSS, JavaScriptStructures, styles, and adds interactivity to webpages

9. Why Understanding the WordPress Technology Stack Matters

Understanding these components is useful even for people who do not write code.

Hosting selection: Website owners can evaluate whether a hosting provider offers compatible PHP and database versions.

Troubleshooting: Understanding the different components makes it easier to identify whether a problem originates in PHP execution, database connectivity, the web server, or WordPress itself.

Performance optimisation: Website performance depends on several factors, including PHP execution, database efficiency, server resources, caching, and frontend optimisation.

Security: Maintaining a secure website requires keeping WordPress, themes, plugins, PHP, the database system, and server software appropriately updated.

Website development: Developers working with WordPress plugins generally need PHP knowledge, database skills, and familiarity with HTML, CSS, and JavaScript.

Website migration: Moving a WordPress website generally involves transferring both its website files and database, followed by configuring the new hosting environment.

Conclusion

WordPress is not simply an independent software package. It is a Content Management System built on top of several complementary technologies.

Its technology stack can be understood through four fundamental functional categories:

  1. Programming Language: PHP executes the instructions that power WordPress.
  2. Database Management System: MySQL or MariaDB stores and retrieves website information.
  3. Content Management System: WordPress brings the underlying capabilities together and provides an interface for managing the website.
  4. Web Server: Apache, Nginx, or LiteSpeed receives requests and delivers website resources and responses.

An operating system provides the underlying environment, while HTML, CSS, and JavaScript help deliver the frontend experience.

Together, these technologies make it possible to build anything from a simple personal blog to a complex business website, digital marketplace, membership platform, or e-commerce store.

Understanding this architecture is an excellent starting point for anyone interested in WordPress development, website hosting, or technical administration.

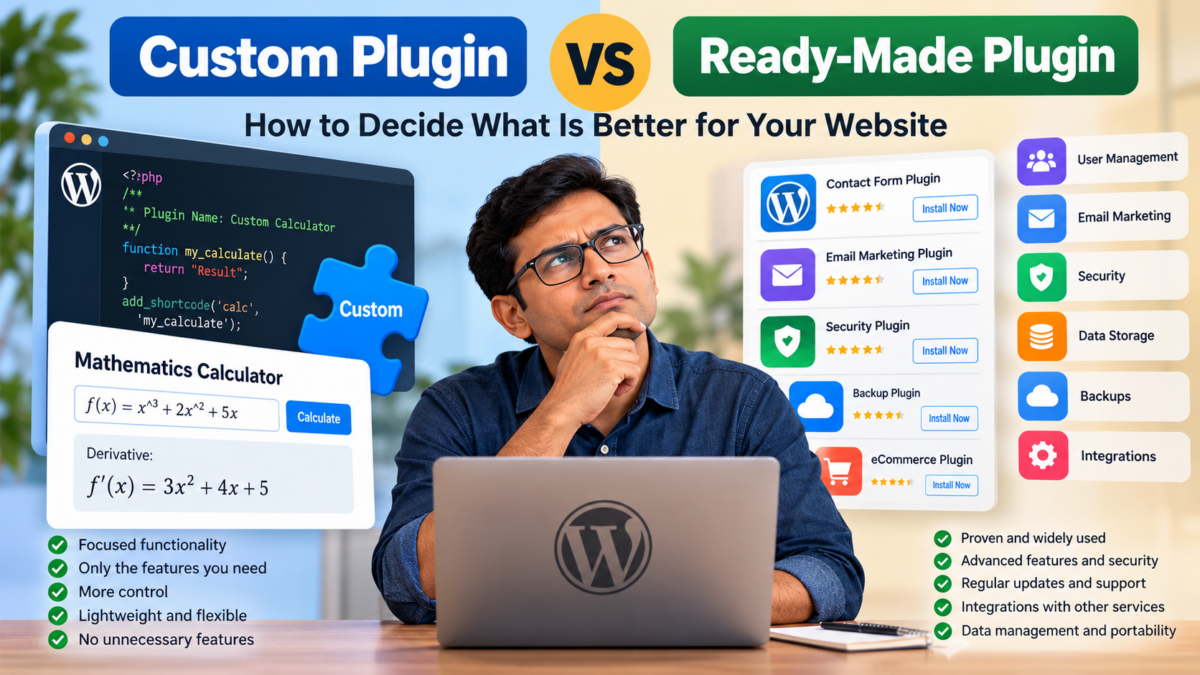
Custom Plugin vs. Ready-Made WordPress Plugin: How to Decide What Is Better for Your Website

When developing a WordPress website, one question frequently arises: Should you develop a custom plugin to fulfil a particular requirement, or should you install an existing free or paid plugin?

At first glance, developing a custom plugin might seem like the more attractive option. You get exactly the functionality you want, avoid unnecessary features, and retain control over the code.

However, there is another side to the equation. A plugin is not always just a collection of features. Depending on its purpose, it may also be responsible for security, data storage, backups, user management, integrations, maintenance and long-term data accessibility.

The decision, therefore, should not be based exclusively on development costs or the number of features.

It should be based on the nature of the functionality, the responsibility the plugin carries, and what happens to the data and services associated with it over time.

Let’s examine the considerations.

1. When a Custom Plugin Makes More Sense

Custom plugin development is particularly attractive when the requirement is specific, self-contained and primarily functional.

Consider a website that publishes mathematics tutorials. The website owner wants to introduce a calculator that can differentiate mathematical expressions.

For example, a visitor enters:

[latex]f(x)=x^3+2x^2+5x[/latex]

The calculator returns:

[latex]f'(x)=3x^2+4x+5[/latex]

Would it make sense to install a large, multipurpose plugin just to provide this functionality?

Probably not.

A lightweight custom plugin could accomplish the task without introducing unnecessary dependencies or features.

Other examples include:

  • A calculator for determining website acquisition costs.
  • A domain renewal date display.
  • A custom pricing calculator.
  • A specialised mathematical equation solver.
  • A shortcode that displays selected website statistics.
  • A custom content display system.
  • A small tool that converts one unit into another.

These functionalities have something in common: their primary responsibility is to perform a specific operation or display particular information.

They generally do not require extensive user management, sophisticated security infrastructure or long-term storage of sensitive customer information.

Advantages of custom development

1. Only the features you need

You don’t have to install a plugin containing dozens of features when you only need one or two.

2. Greater control

You decide how the functionality works, how it looks and how it integrates with your website.

3. Less unnecessary complexity

A focused plugin can be easier to maintain than a large multipurpose solution.

4. Freedom to evolve

You can introduce new features as your requirements change without waiting for the original plugin developer.

5. No unnecessary recurring licence fees

You avoid paying for premium features that you might never use.

However, custom development does not automatically mean better performance or security. Poorly written custom code can introduce vulnerabilities, compatibility problems and maintenance headaches.

A custom plugin still needs proper development practices, testing and updates.

2. When an Established Plugin Is the Better Choice

Now consider a different situation.

Suppose you operate a website that collects email addresses through subscription forms.

Initially, you might think that developing a custom plugin to collect email addresses and store them in a WordPress database would be straightforward.

After all, the basic functionality appears simple:

  1. Display a subscription form.
  2. Collect an email address.
  3. Store it in a database.
  4. Allow the administrator to view subscribers.

But this is where the real complexity begins.

What happens when thousands of people subscribe?

What happens when someone wants to unsubscribe?

How do you prevent spam registrations?

How do you secure subscriber information?

How do you manage consent and privacy requirements?

How do you export the subscriber list?

How do you handle backups?

What happens if your hosting provider suspends your account?

What happens if your website is compromised?

And perhaps most importantly, what happens if you eventually close the website?

Suddenly, the seemingly simple plugin has become a data management system.

This is where an established solution may offer considerably more value.

For example, dedicated email marketing platforms and established WordPress plugins often provide:

  • Subscriber management.
  • Email verification.
  • Unsubscribe mechanisms.
  • Spam protection.
  • Data export.
  • Subscriber segmentation.
  • Email campaign management.
  • Security mechanisms.
  • Backup and recovery options.
  • Integration with other platforms.

Recreating all these capabilities independently could require considerable development effort.

More importantly, you would become responsible for maintaining them.

The importance of data independence

This brings us to an especially important consideration.

Your website and your business data should not necessarily depend on each other.

Imagine that you operate a website for five years and accumulate 20,000 subscribers.

Eventually, you decide to discontinue the website.

Does that mean you should lose access to your subscriber database?

Absolutely not.

The subscriber list might still have considerable business value. You may want to transfer it to another website, use it for a different business, or migrate it to another email marketing platform, subject to applicable consent and privacy requirements.

This is one reason why dedicated platforms can be attractive.

If subscriber information is maintained independently of your website, closing the website does not necessarily mean losing access to the information.

However, there is an important distinction: not every popular WordPress plugin provides independent data storage.

Some plugins store everything inside your WordPress database. If your hosting account disappears and you have no backup, the data may disappear with it.

Therefore, choosing an established plugin is not enough. You must examine its data portability and storage arrangements.

3. Security Is More Than Writing Secure Code

Security is another important factor when deciding between custom and established plugins.

A developer might write a perfectly functional plugin that performs its intended task.

But does that automatically make it secure?

Not necessarily.

Security involves considerably more than preventing SQL injection or sanitising user input.

Depending on the plugin’s responsibilities, security may involve:

  • User authentication and authorisation.
  • Protection against cross-site scripting.
  • Protection against SQL injection.
  • Nonce verification.
  • Rate limiting.
  • Spam prevention.
  • Secure API communication.
  • Access control.
  • Data encryption where appropriate.
  • Regular vulnerability assessments.
  • Security updates.

If a custom plugin simply calculates mathematical expressions without collecting personal information, its security requirements are relatively limited.

However, if it processes payments, manages customer accounts, stores personal information or handles business transactions, the requirements become substantially more demanding.

An established plugin with a strong development team, a history of security updates and a responsible vulnerability disclosure process may be a more sensible choice.

Nevertheless, popularity alone is not proof of security.

A widely installed plugin can still contain vulnerabilities, and an abandoned plugin can become a liability.

The important consideration is the quality of its maintenance and security practices.

4. Consider What Happens When the Website Closes Down

This is an area that deserves considerably more attention.

Website owners frequently evaluate plugins based on their immediate requirements.

They ask:

  • Does it work?
  • Is it compatible with my theme?
  • Does it provide the required features?
  • Is it free?
  • Does it slow down my website?

These are reasonable questions, but they overlook an important issue:

What happens to the functionality and data when the website is discontinued?

Consider three examples.

Plugin functionalityWhat happens when the website closes?
Mathematical calculatorThe functionality becomes unavailable, but there may be no valuable user data to recover.
Contact management systemCustomer information may need to be exported and retained securely.
Email subscriber managementSubscriber information may need to be migrated to another platform, subject to consent and privacy obligations.

The distinction is significant.

A calculator is primarily a functional asset.

A subscriber database is a business asset.

A payment processing system may be part of a critical business operation.

The more important the underlying data and business processes, the more carefully you should evaluate the infrastructure supporting them.

For critical information, consider maintaining independent backups, regular exports and a migration strategy.

Do not assume that installing a popular plugin automatically provides these safeguards.

5. The Hidden Cost of Maintaining a Custom Plugin

One of the biggest misconceptions about custom development is that the cost ends when the plugin is completed.

It doesn’t.

A custom plugin becomes another software component that someone must maintain.

Consider the following responsibilities:

ResponsibilityWhat it involves
WordPress compatibilityTesting against newer WordPress releases.
PHP compatibilityEnsuring the plugin works with updated PHP versions.
SecurityIdentifying and fixing vulnerabilities.
Database maintenanceManaging schema changes and data integrity.
Third-party integrationsUpdating APIs when external services change.
Bug fixesResolving unexpected behaviour.
DocumentationMaintaining technical documentation.
TestingEnsuring new changes do not break existing functionality.

These responsibilities become particularly important when a plugin is used across multiple websites.

An established plugin may distribute these maintenance responsibilities across a dedicated development team and a larger user base.

With a custom plugin, the responsibility generally falls on its owner or developer.

This does not mean custom development is necessarily more expensive.

A small, stable plugin might require very little maintenance.

But a complex custom system can eventually become considerably more expensive than purchasing an established solution.

6. Free vs. Paid Plugins: Another Important Distinction

It is also worth distinguishing between free and paid plugins.

A free plugin is not necessarily inferior to a paid one.

Many excellent WordPress plugins are available without charge.

However, paid plugins sometimes offer additional benefits:

  • Dedicated technical support.
  • Regular updates.
  • Advanced functionality.
  • Better integrations.
  • Premium security features.
  • Professional documentation.
  • Commercial maintenance commitments.

When evaluating a paid plugin, examine what the licence actually provides.

Does the subscription cover updates only, or does it include support?

What happens when the subscription expires?

Will the plugin continue functioning?

Can you continue using the installed version?

Can you export your data?

These questions are particularly important when a plugin becomes integral to your business.

A paid plugin should not be selected merely because it carries a price tag. Its ongoing value must justify the expenditure.

7. A Hybrid Approach Might Be the Best Solution

There is another possibility that website owners sometimes overlook.

You do not necessarily have to choose between developing everything yourself and installing an existing plugin for everything.

A hybrid approach can offer the best of both worlds.

For example, suppose you operate a website that provides mathematics tutorials.

You might use:

  • A custom plugin for mathematical calculators.
  • An established SEO plugin for search optimisation.
  • A dedicated email marketing platform for subscriber management.
  • An established security plugin for website protection.
  • A recognised backup solution for disaster recovery.
  • A custom plugin for displaying specialised website analytics.

This arrangement allows you to develop features that differentiate your website while relying on established solutions for infrastructure-intensive responsibilities.

There is little reason to reinvent functionality that is already available, tested and maintained by experienced developers.

At the same time, there is no reason to install an unnecessarily large plugin when a small custom solution can accomplish the task more efficiently.

8. A Practical Decision Framework

The following table summarises how website owners can approach the decision.

RequirementRecommended approach
Simple mathematical calculatorCustom plugin
Specialised pricing calculatorCustom plugin
Custom shortcode or display functionalityCustom plugin
Domain information displayCustom plugin
Complex membership managementEstablished plugin
Email subscriber managementEstablished platform or plugin
Payment processingEstablished payment provider and integration
Customer relationship managementEstablished CRM
Security infrastructureEstablished, actively maintained solution
Backup and recoveryEstablished backup solution
Complex e-commerce functionalityEstablished e-commerce platform
Specialised business workflowHybrid approach

These are general recommendations rather than absolute rules.

For example, a custom membership system might be justified for a highly specialised application, provided the organisation has the resources to maintain it.

Similarly, a simple subscriber collection form might be developed as a custom plugin if it integrates with an established email marketing service rather than storing and managing subscribers independently.

The distinction is between developing the interface or specialised functionality and taking responsibility for the entire underlying infrastructure.


9. Think Beyond the Initial Development Cost

Perhaps the most important lesson is that plugin selection should be treated as a long-term business decision.

Imagine two scenarios.

Scenario A: Custom development

You spend ₹10,000 developing a custom plugin that performs exactly the function you need.

It works perfectly, and you retain complete control over its functionality.

But three years later, WordPress or PHP changes, and the plugin requires modifications.

You must find a developer, pay for the work and test the updated version.

Scenario B: Established solution

You pay for an established plugin with an annual licence.

The initial and recurring expenditure might be higher.

However, the developer maintains compatibility, provides updates and offers technical support.

Neither scenario is automatically better.

If the custom plugin is small and stable, Scenario A could be considerably more economical.

If the plugin handles critical business operations, Scenario B might offer better long-term value.

The correct comparison is therefore not simply:

Custom development cost vs. plugin purchase price.

It is:

Total cost of ownership vs. the value, reliability and independence provided by the solution.

This includes development, licensing, hosting, storage, maintenance, support, security and eventual migration costs.

Conclusion: Develop What Differentiates You, Adopt What Protects Your Business

The decision to develop a custom plugin or use an established solution should depend primarily on what the plugin is expected to accomplish.

If the requirement is a focused functionality, such as calculating derivatives, displaying domain information or generating specialised reports, custom development can be an excellent choice.

It offers flexibility, control and the freedom to avoid unnecessary features.

However, when a plugin becomes responsible for managing subscribers, customer information, payments, memberships, security or other critical business operations, the decision becomes more complicated.

In such cases, established solutions may provide a more practical foundation because they can offer mature infrastructure, ongoing maintenance, integrations and data management capabilities.

There is also a particularly important consideration: the long-term independence of your data.

A website might eventually be discontinued, but its business information could remain valuable for years.

Therefore, data portability, independent backups and migration options deserve as much attention as the plugin’s immediate functionality.

Ultimately, a sensible principle to follow is:

Build the functionality that makes your website unique. Adopt established solutions for infrastructure that requires continuous security, reliability and specialised maintenance.

And where necessary, combine the two.

The objective should not be to minimise the number of plugins or maximise custom development. It should be to build a website that remains manageable, secure, economical and sustainable over the long term.

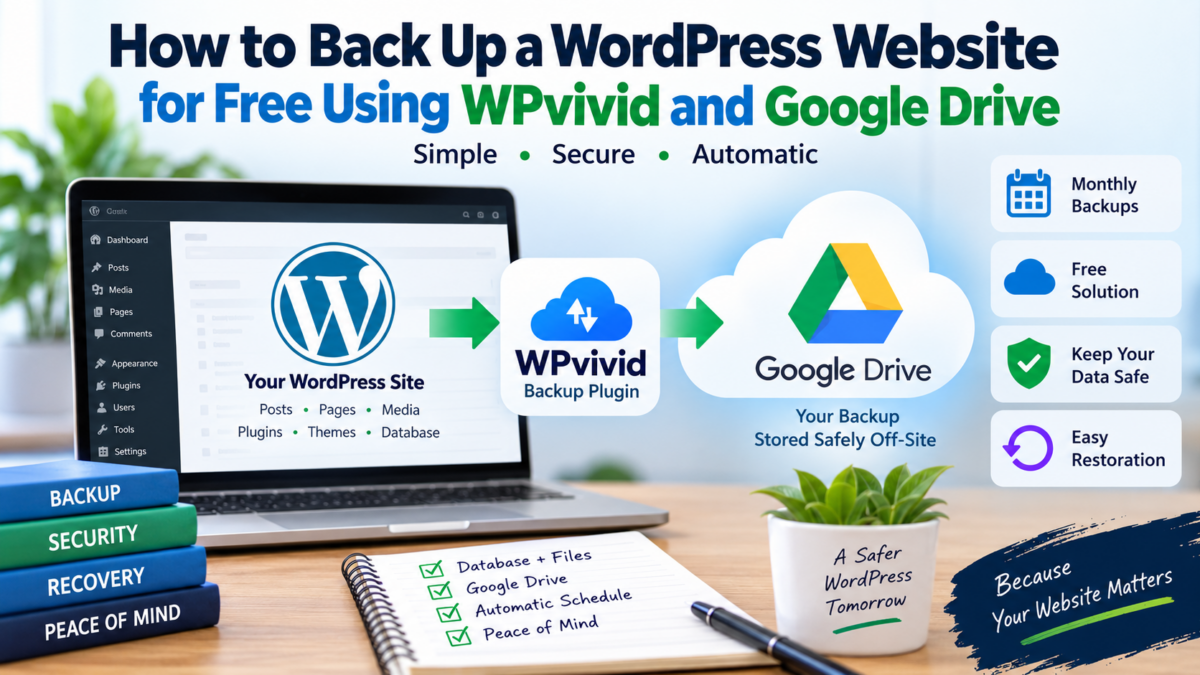
How to Back Up a WordPress Website for Free Using WPvivid and Google Drive

A WordPress website can represent months or even years of work. Posts, pages, images, plugins, themes, settings, and database records can all be lost if something goes wrong with the hosting server.

Fortunately, you don’t necessarily need to pay for a separate backup service.

In this guide, we’ll set up a free WordPress backup system using WPvivid Backup Plugin and Google Drive. The setup is simple enough for a small business website, blog, portfolio site, or WordPress-based marketplace.

I recently used this approach to set up a backup system for a WordPress website, and the complete process was straightforward: create a full backup, connect Google Drive, test an off-site backup, and then schedule automatic monthly backups.


Why You Should Keep an Off-Site Backup

Many WordPress hosting companies provide some form of backup. However, relying exclusively on a backup stored on the same hosting server isn’t ideal.

Imagine that your website and its backup are both stored on the same server. If there is a serious server failure or you lose access to the hosting account, the backup may not be available when you need it.

This is why an off-site backup is useful.

Instead of keeping the only backup here:

WordPress website → Hosting server

we can have:

WordPress website → Hosting server + Google Drive

The second copy is stored separately from the website.

WPvivid’s documentation specifically recommends remote storage for additional protection against server failures and hosting problems. (WPvivid Documentation)


What We Will Use

For this setup, we need:

  1. A WordPress website
  2. The free version of WPvivid Backup & Migration
  3. A Google account with Google Drive
  4. A few minutes to configure the backup

You can find WPvivid in the official WordPress plugin directory:

WPvivid Backup & Migration on WordPress.org

WPvivid’s free version supports manual backups, scheduled backups, remote storage and restoration. Its supported remote storage options include Google Drive, Dropbox, OneDrive, Amazon S3 and FTP/SFTP. (WPvivid Documentation)


Step 1: Install WPvivid

From your WordPress dashboard, go to:

Plugins → Add New

Search for:

WPvivid Backup & Migration

Install and activate the plugin.

After activation, you should see WPvivid Backup in your WordPress dashboard.


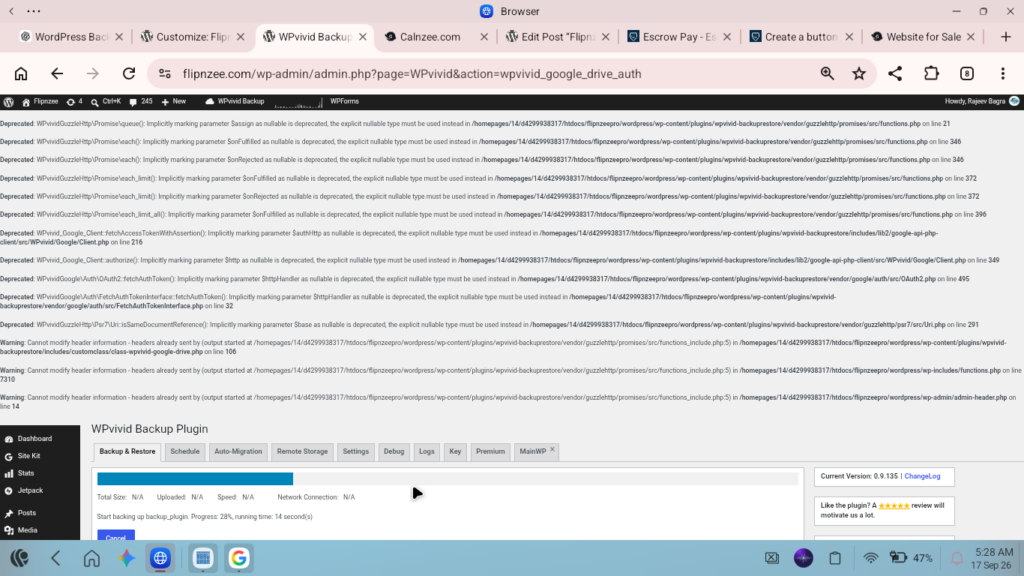
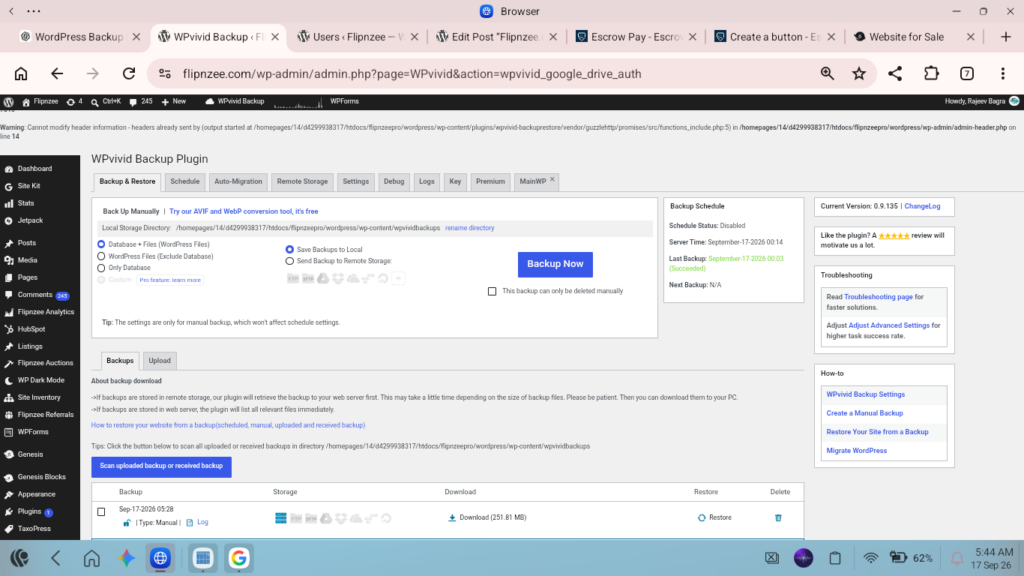
Step 2: Create Your First Full Backup

Before configuring automatic backups, I recommend creating a manual backup.

Open:

WPvivid Backup → Backup & Restore

Choose:

Database + Files (WordPress Files)

This is a full backup.

A full WordPress backup includes both the database and website files. The database contains important information such as posts, pages, users and plugin settings, while the files include themes, plugins and uploaded media. (WPvivid Documentation)

For a business website or marketplace, I would generally choose the full Database + Files option rather than backing up only the database.

Then click:

Backup Now

Wait for the process to finish.

Do not close the page or cancel the backup while it is running.


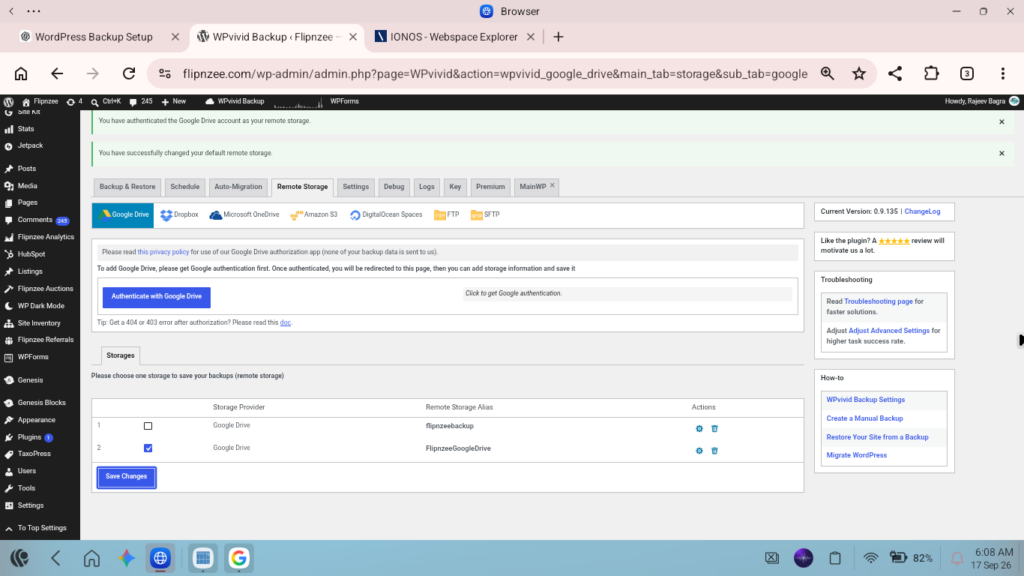
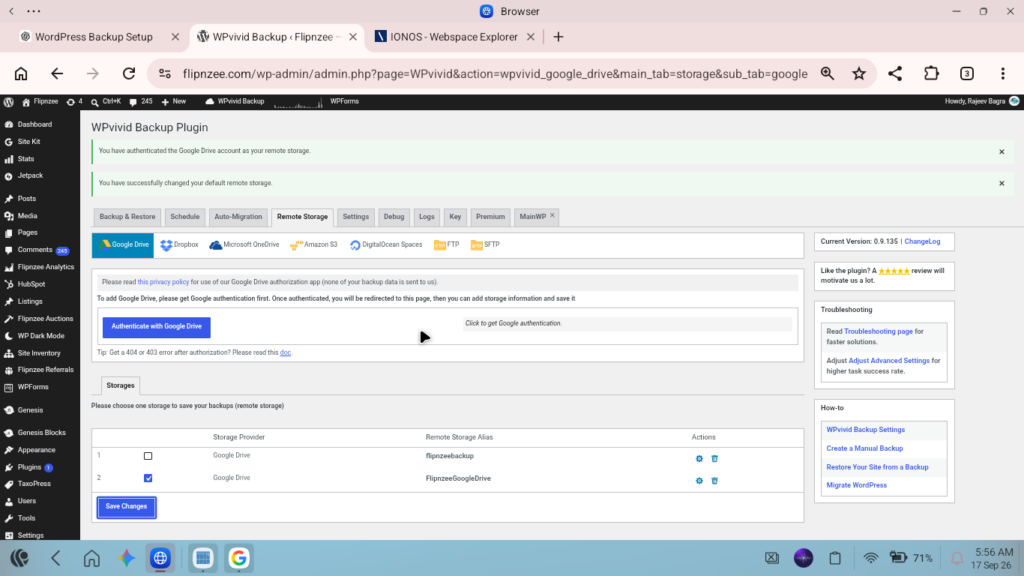
Step 3: Connect Google Drive

Once the manual backup has completed, go to:

WPvivid Backup → Remote Storage

Select:

Google Drive

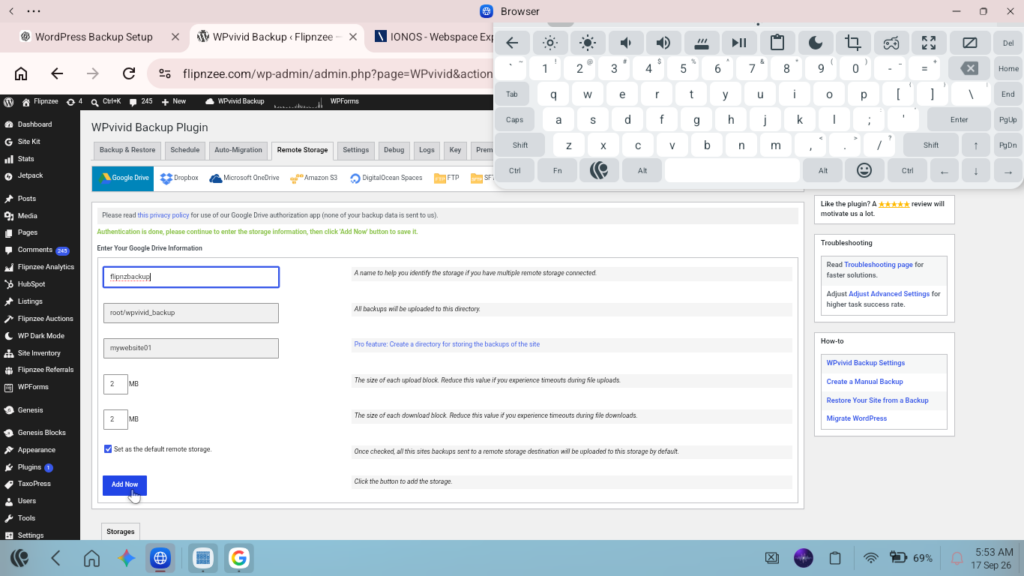
WPvivid will ask you to authenticate your Google account.

Follow the Google authorization process and return to WordPress.

WPvivid officially supports Google Drive as a remote backup destination. (WPvivid Documentation)

After authentication, Google Drive should appear in the list of available remote storage options.


Step 4: Make Google Drive the Default Remote Storage

If you have more than one remote storage connection, select the Google Drive account you want to use as the default storage destination.

For example, you might give the connection a recognizable name such as:

My Website Google Drive

The exact name isn’t important. It is simply an identifier that helps you recognize the storage connection later.

Once Google Drive is selected as the default remote storage, scheduled backups can use that destination.


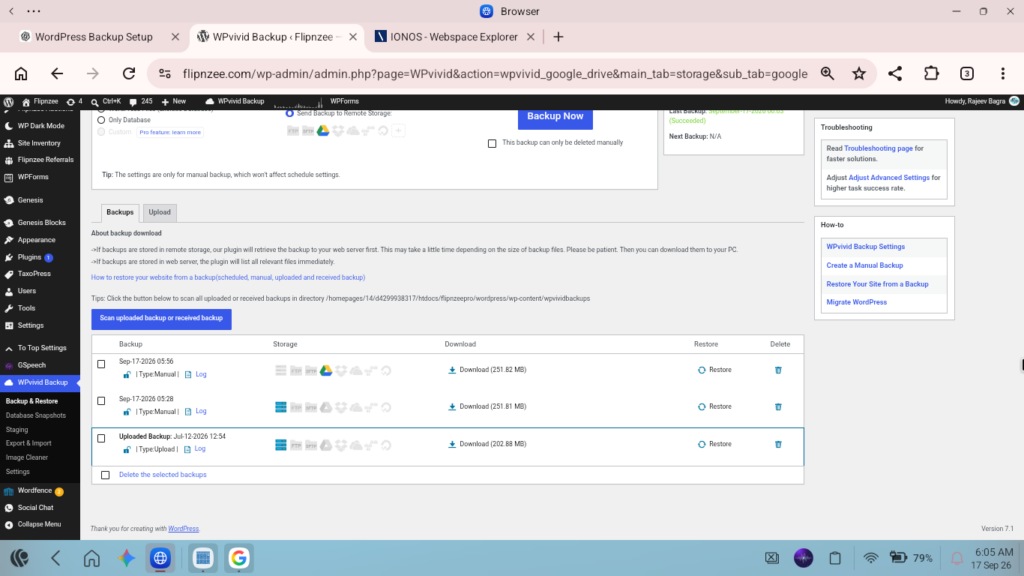
Step 5: Test a Real Google Drive Backup

This is an important step.

Don’t assume that because Google Drive has been connected, everything is working.

Go back to:

WPvivid Backup → Backup & Restore

Select:

Database + Files (WordPress Files)

Then select:

Send Backup to Remote Storage

Make sure Google Drive is selected.

Click:

Backup Now

Wait until the backup finishes.

Then check the backup list.

You should see the newly created backup and Google Drive should appear as the remote storage destination.

This test confirms that the complete process works:

WordPress → WPvivid → Google Drive

WPvivid supports both manual backups and cloud-storage destinations. (WPvivid)


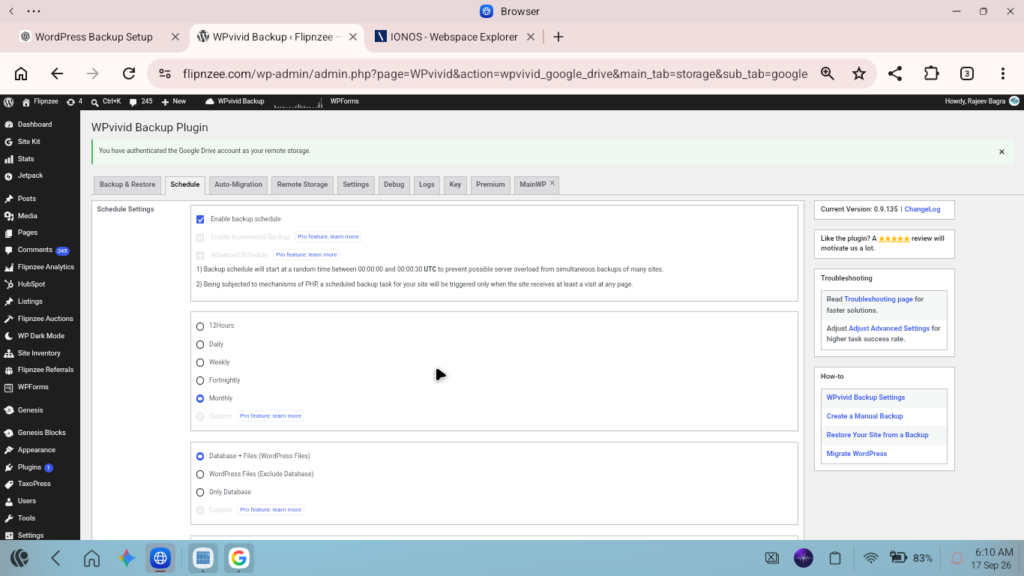
Step 6: Set Up Automatic Backups

Once the manual Google Drive backup has been successfully tested, it’s time to automate the process.

Go to:

WPvivid Backup → Schedule

Enable:

Enable backup schedule

WPvivid provides several scheduling options, including daily, weekly, fortnightly and monthly backups. (WPvivid Documentation)

For a website that doesn’t change dramatically every day, monthly full backups can be a simple and practical arrangement.

Select:

Monthly

Then select:

Database + Files (WordPress Files)

And select:

Send backups to remote storage

Make sure your Google Drive storage is selected.

Finally, click:

Save Changes


My Recommended Basic Configuration

For a small business website or WordPress project, a simple configuration could look like this:

SettingRecommended option
Backup frequencyMonthly
Backup typeDatabase + Files
DestinationGoogle Drive
Backup methodAutomatic
Manual backupBefore major changes

This isn’t the only possible configuration. Websites that change frequently may benefit from more frequent backups.

WPvivid itself notes that backup frequency can be adjusted according to how frequently a website changes. (WPvivid)


Don’t Forget Manual Backups

Automatic monthly backups are useful, but I wouldn’t rely on them exclusively.

Before making a major change to your WordPress website, create a manual backup.

For example, create a backup before:

  • Updating WordPress
  • Installing a major plugin
  • Changing your theme
  • Making significant database changes
  • Performing a migration
  • Modifying custom code
  • Making major changes to a custom WordPress plugin

This gives you a restore point immediately before the change.

WPvivid specifically identifies manual backups as useful before WordPress updates, plugin/theme changes, configuration changes and migrations. (WPvivid Documentation)


Why I Prefer Database + Files

You may notice that WPvivid gives you several choices:

Database + Files

WordPress Files

Only Database

These have different purposes.

Database only

This protects your WordPress database but doesn’t contain all your website files.

It can be useful in certain situations, but it isn’t sufficient as your only disaster-recovery backup.

WordPress files only

This protects files such as:

  • Themes
  • Plugins
  • Images
  • Uploaded documents
  • Other WordPress files

But it doesn’t protect the database.

Database + Files

This combines both.

For a complete website recovery strategy, this is generally the option I would choose.

WPvivid describes a full backup as a backup containing both the website files and database. (WPvivid Documentation)


Why Google Drive Is Useful

The biggest advantage isn’t necessarily Google Drive itself.

The important concept is separation.

Your website is hosted in one location while the backup is stored somewhere else.

For example:

Website

→ Hosting server

Backup

→ Google Drive

If something happens to the hosting server, you have another copy outside that server.

WPvivid describes remote storage as a way to provide off-site protection and additional backup redundancy. (WPvivid Documentation)


One Important Limitation: Backup Frequency

A monthly backup is convenient, but consider how frequently your website changes.

Suppose your website changes significantly every week and you only create one backup each month.

If something goes wrong near the end of the month, your most recent backup could be several weeks old.

For a frequently updated website, you may therefore prefer:

Daily → Weekly → Fortnightly

rather than monthly.

For a relatively stable website, monthly may be perfectly adequate.

The right frequency depends on how much data you can afford to lose between backup points.


Keep Multiple Backup Versions

Another useful practice is to retain several backup versions rather than continuously replacing one backup with another.

For example:

  • Current month’s backup
  • Previous month’s backup
  • Backup from two months ago
  • Backup from three months ago
  • etc.

This gives you several restore points.

It’s particularly useful if you discover a problem only after several days or weeks.

WPvivid provides backup-retention settings for controlling how many backup copies are kept. (WPvivid)


Test Your Backups

A backup is only useful if you can actually restore from it.

After establishing your backup system, periodically verify that:

  1. The backup is being created.
  2. The backup reaches Google Drive.
  3. The backup appears in WPvivid.
  4. The backup can be downloaded or accessed.
  5. You understand how to restore the website.

You don’t necessarily need to restore your live website just to test the process. If you have a staging or test environment, that can be a safer place to test restoration.


A Simple Backup Strategy for WordPress

For many website owners, the following approach is easy to maintain:

Normal operation

Automatic monthly full backup

↓

Google Drive

↓

Keep several previous backup copies

Before major changes

Manual full backup

↓

Google Drive

↓

Make the website/plugin changes

This gives you both routine protection and a backup immediately before important work.


What About WordPress Plugin Code?

If your website contains custom-developed plugins, there is another important consideration.

A WordPress backup protects the installed plugin files, but I would also recommend keeping the source code under version control, especially for custom plugins.

For example:

WordPress backup

→ Protects the working website and database

Git repository

→ Protects the development history and source code

These solve different problems and complement each other.


Final Thoughts

You don’t need an expensive backup system to get started with proper WordPress backup protection.

A straightforward setup can be:

WPvivid Free

↓

Full Database + Files backup

↓

Google Drive

↓

Automatic monthly schedule

↓

Manual backup before major changes

WPvivid’s free plugin officially supports scheduled backups and remote storage, including Google Drive. (WPvivid Documentation)

The most important lesson is simple:

Don’t keep your only backup on the same server as your website.

An off-site copy gives you another recovery option if your hosting environment becomes unavailable.

For more detailed instructions, the official resources are:

WPvivid Backup & Migration – Official Website

WPvivid Backup Documentation

WPvivid on WordPress.org

AI Coding Agents Didn’t Make Software Engineering Obsolete—They Changed Where the Value Lies

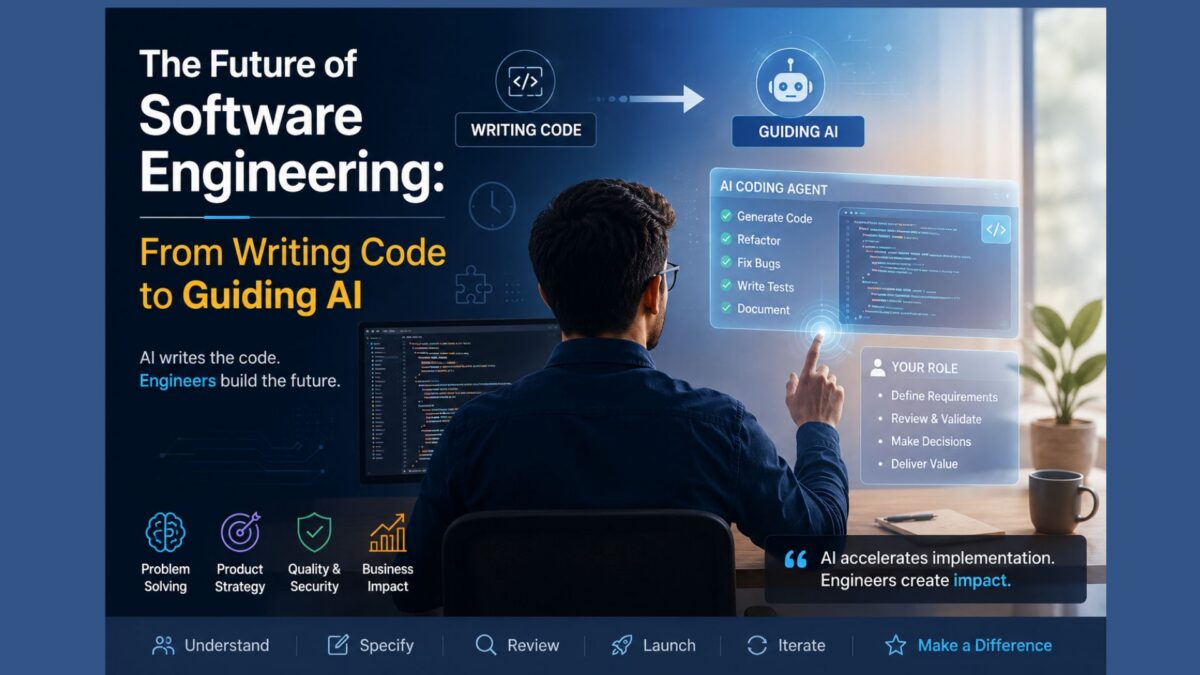
For many developers, the emergence of AI coding agents has prompted an uncomfortable question: Was all the time spent learning software development worth it if AI can now generate working code in minutes?

A recent reflection on the development of the Flipnzee Auctions plugin offers an interesting perspective.

The project began as a learning exercise. Rather than rushing to release a product, its development progressed step by step, covering WordPress plugin architecture, object-oriented PHP, database design, AJAX, scheduled tasks, payment workflows, Git, debugging, and software organization. Every feature became an opportunity to understand not just what to build, but why it should be built that way.

Looking back, there is no denying that modern AI coding agents can now perform many of these implementation tasks remarkably quickly. Refactoring classes, generating CRUD interfaces, organizing project structures, fixing common bugs, writing documentation, and even producing test cases are increasingly becoming tasks that can be completed in minutes rather than days.

At first glance, this might suggest that months of development effort were unnecessary.

The reality is more nuanced.

The greatest value of the project was never the number of lines of PHP that were written. It was the understanding gained throughout the process.

By building the plugin manually, the developer learned how WordPress hooks interact, how database migrations work, why security checks matter, how to organize maintainable code, how to debug complex issues, and how seemingly small architectural decisions affect future development.

These lessons cannot simply be downloaded from an AI.

Ironically, this experience makes AI significantly more valuable rather than less. Someone who understands software engineering can evaluate AI-generated code, recognize hidden bugs, identify security concerns, and determine whether a suggested implementation truly fits the product.

Without that understanding, generated code often becomes little more than a black box.

There is, however, an important lesson for startups.

While the educational value of building software from scratch is enormous, there is also a point of diminishing returns. Projects can become trapped in endless cycles of refactoring, redesigning, and documenting instead of reaching users.

Many founders discover that they spend more time perfecting architecture than validating whether customers actually want the product.

In hindsight, a more balanced approach may have been to release an early version, gather feedback, and allow AI to accelerate subsequent iterations.

This highlights the real shift brought about by modern coding agents.

The competitive advantage is no longer typing code faster than everyone else.

The competitive advantage lies in identifying worthwhile problems, designing practical solutions, specifying clear requirements, reviewing AI-generated implementations, and continuously improving the product based on real-world feedback.

For developers who have invested years in learning programming, this should be encouraging rather than discouraging.

Their knowledge has not lost its value.

Instead, the nature of their work has evolved.

As AI increasingly handles implementation, software engineers move higher up the value chain—focusing on product strategy, architecture, user experience, quality assurance, and business decisions.

The future belongs not to those who write every line of code manually, nor to those who rely entirely on AI, but to those who can combine engineering judgment with AI-assisted development.

In many ways, learning software engineering has become more valuable than ever—not because developers must write every function themselves, but because they now possess the expertise to guide AI toward building better software.

Lesson 135 – Flipnzee Auctions Is Now a Working Product: Lessons Learned and Future Roadmap


Introduction

When this lesson series began, the objective was simple: build a WordPress auction plugin while learning professional plugin development.

Over the course of 135 lessons, that objective gradually evolved.

Instead of producing a tutorial project, the result is a functional auction plugin designed specifically for buying and selling websites, domains, and other digital assets.

Although there are still many possible enhancements, the plugin has reached a point where it can already support real marketplace transactions.

This final lesson summarizes what has been built, the architectural decisions made throughout the series, and where future development may lead.


Looking Back

The project started with a single goal:

Learn WordPress plugin development by building something practical.

Instead of isolated code examples, every lesson contributed to a growing production codebase.

Along the way we explored:

  • WordPress plugin architecture
  • Object-oriented PHP
  • Custom database tables
  • WordPress hooks and filters
  • Secure form handling
  • Shortcodes
  • REST APIs
  • Transaction workflows
  • External provider integrations
  • Database migrations
  • Refactoring techniques
  • Maintainable software design

The result is not merely a collection of lessons but a complete working project.


What the Plugin Already Supports

Today Flipnzee Auctions includes support for:

Auction Management

  • Create auctions
  • Edit auctions
  • Delete auctions
  • Schedule auctions
  • Automatically activate auctions
  • Automatically close expired auctions

Bidding

  • Secure bid placement
  • Highest bidder tracking
  • Bid validation
  • Reserve price support
  • Anti-sniping auction extensions
  • Winner determination

Marketplace

  • Active auction listings
  • Recently closed auctions
  • Analytics summaries
  • Listing thumbnails
  • Countdown timers
  • Buy Now pricing
  • Watchlists

Buyer Experience

  • Buyer Dashboard
  • My Purchases
  • Purchase Details
  • Transaction history
  • Transfer progress

Transaction Management

  • Automatic transaction creation
  • Transaction lifecycle
  • Payment workflow
  • State management
  • Activity logging
  • Notifications

Transfer Workflow

Support for tracking:

  • Payment
  • Website files
  • Database
  • Domain transfer
  • Buyer verification

External Providers

The architecture already supports integration with external services.

Current work includes:

  • Escrow provider abstraction
  • External Provider Manager
  • Escrow API client
  • Provider lifecycle management

Although currently operating in simulation or staged workflows, the underlying architecture has been designed so that additional providers can be added in the future with minimal disruption.


Why Development Slowed Near the End

As the plugin matured, a different question emerged.

Instead of asking:

“Can another feature be built?”

the more important question became:

“Should another feature be built right now?”

There is an important difference.

Software development becomes significantly more valuable when guided by real users rather than assumptions.


The Next Stage Is Validation

The plugin is now capable of supporting real marketplace listings.

Rather than immediately implementing every planned feature, the focus shifts to understanding how buyers actually interact with the marketplace.

Questions that only real users can answer include:

  • Do buyers prefer bidding or Buy Now?
  • How often do negotiations occur before a purchase?
  • Does verified analytics increase buyer confidence?
  • Which information influences purchasing decisions most?
  • Which parts of the purchase workflow deserve automation?

Answers to these questions cannot be discovered through programming alone.

They require real marketplace activity.


Features Deferred Intentionally

Several ideas remain on the roadmap, including:

  • Dedicated Buy Now purchase pages
  • Dynamic Escrow checkout generation
  • Multiple payment providers
  • Stripe integration
  • PayPal integration
  • Wise support
  • Cryptocurrency payments
  • Seller dashboards
  • Public seller onboarding
  • Offer and negotiation workflows
  • Messaging between buyers and sellers
  • Automated transfer checklists
  • Public marketplace analytics

None of these ideas have been abandoned.

They have simply been postponed until real usage demonstrates their value.


An Important Lesson

One of the biggest lessons learned during this project is that good software is not defined by the number of features it contains.

Good software solves real problems while remaining understandable and maintainable.

Throughout the series there were many occasions where existing code was refactored instead of adding new functionality.

Those refactoring lessons were just as valuable as implementing new features because they improved the long-term quality of the project.


The Plugin Is No Longer Just a Tutorial

Although these lessons were written as an educational series, the project gradually became something more.

Flipnzee Auctions is now:

  • a learning resource for WordPress developers,
  • a reference implementation for plugin architecture,
  • and a functional marketplace plugin capable of supporting real website sales.

Future improvements will continue to be driven by practical experience rather than simply expanding the feature list.


Final Thoughts

Building software is rarely about reaching a finish line.

Instead, each release represents a milestone in an ongoing process of learning, refinement, and adaptation.

This lesson series demonstrates that a complex WordPress plugin can be developed incrementally through small, understandable improvements while maintaining a working codebase throughout the journey.

The next chapter for Flipnzee Auctions is no longer primarily about writing code.

It is about observing real users, learning from actual marketplace transactions, and allowing those experiences to guide future development.

For anyone who followed this series from the beginning, thank you for joining the journey. Hopefully it has shown that large software projects are not built in a single leap—they are created one carefully considered lesson at a time.


Series Conclusion

With this lesson, the initial Flipnzee Auctions development series comes to a close.

Future articles will focus less on building features in isolation and more on maintaining, improving, and evolving the plugin based on real-world experience. That transition—from development to product stewardship—is a natural step in the lifecycle of any software project and, arguably, one of the most valuable lessons of all.

Lesson 134: Refactoring the Winner Determination Workflow (Implementation)

Introduction

In the previous lesson, we analyzed the complete winner determination workflow and discovered that several responsibilities had gradually accumulated inside the Bid Manager.

While debugging the missing transaction creation, it became clear that the underlying issue was not the Transaction Manager or the Escrow integration. Instead, the winner determination process itself had become increasingly difficult to follow due to duplicated logic and mixed responsibilities.

The objective of this lesson was therefore to refactor the workflow before introducing any new marketplace functionality.


Problems Identified

During the review we identified several issues.

  • Reserve price validation appeared in multiple places.
  • Winner determination and reserve checking were tightly coupled.
  • The workflow was difficult to trace from auction completion to transaction creation.
  • Debugging required following several nested function calls.
  • Future payment integrations would become increasingly difficult.

Rather than continuing to build on top of this complexity, the decision was made to simplify the workflow.


Refactoring Goals

The refactoring focused on three objectives.

Single Responsibility

Each function should perform one task.

For example:

  • Determine winner
  • Validate reserve price
  • Fire events
  • Create transaction

should all remain separate operations.


Clear Event Flow

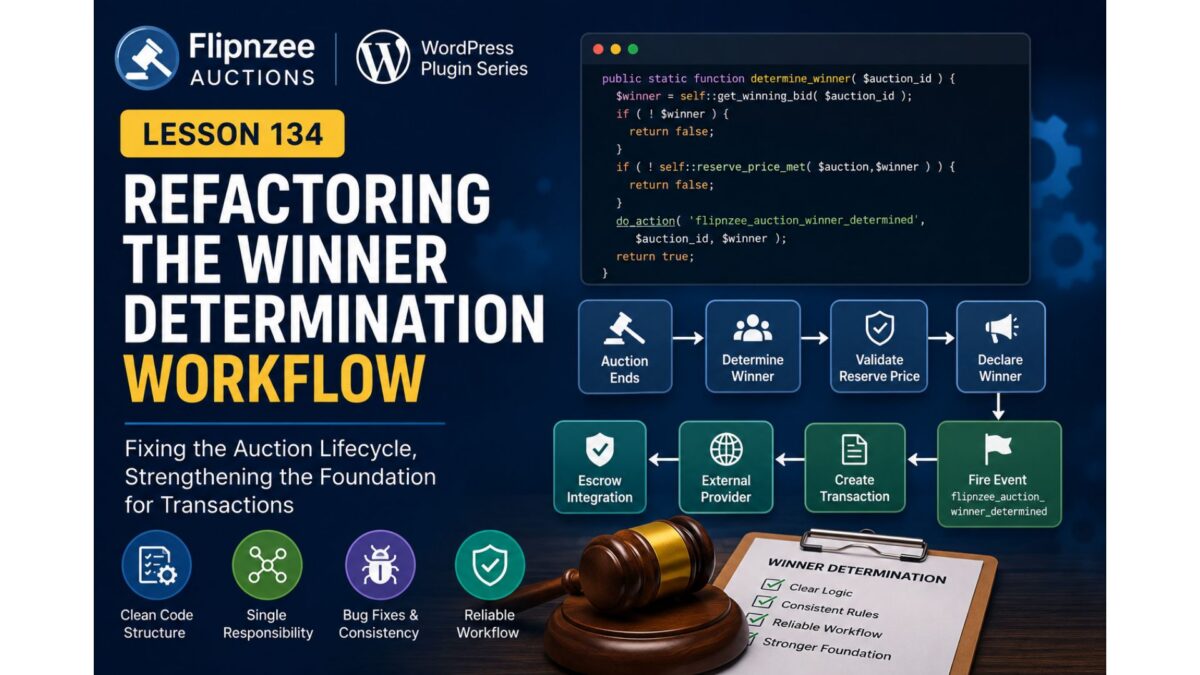
The winner determination process now follows a predictable sequence.

Auction Ends
      │
      ▼
Determine Highest Bid
      │
      ▼
Validate Reserve Price
      │
      ▼
Declare Winner
      │
      ▼
Fire Winner Event
      │
      ▼
Transaction Manager
      │
      ▼
External Provider Manager
      │
      ▼
Escrow API Client

Easier Debugging

Instead of wondering whether the Transaction Manager was malfunctioning, it became possible to inspect the workflow step by step.

Each stage now represents a clear transition in the auction lifecycle.


Why This Matters

Although this refactoring produced very little visible change on the frontend, it significantly improved the internal architecture.

A well-defined event flow makes it easier to:

  • integrate new payment providers
  • add notifications
  • automate transactions
  • create audit logs
  • support additional marketplace features

without repeatedly modifying the Bid Manager.


Result

The Flipnzee Auctions plugin now has a cleaner winner determination workflow that separates auction logic from payment processing.

This architectural improvement provides a stable foundation for the next phase of development, where the marketplace begins evolving beyond simple bidding into a complete purchasing experience.


Next Lesson

In the next lesson we begin connecting auctions with secure payments by redesigning the Buy Now workflow around Escrow.com.

Rather than treating Buy Now as the end of the auction, it will become the beginning of a secure purchasing process.

Lesson 134: Refactoring the Winner Determination Workflow

As the Escrow integration matured, testing uncovered an unexpected issue. Although the transaction management architecture had been significantly improved, transaction creation was still not occurring when an auction completed. Rather than immediately assuming the problem existed inside the new transaction code, a systematic review of the auction lifecycle was performed.

This lesson documents the investigation, identifies the true source of the problem, and begins refactoring the winner determination workflow.


The Initial Symptoms

The plugin loaded successfully.

The logs confirmed:

  • Auction Manager initialized.
  • Escrow Provider initialized.
  • Transaction Manager instantiated.

However, one important log entry never appeared:

FLIPNZEE: create_transaction_from_auction() started.

This indicated that the transaction manager itself was not the source of the problem.


Following the Execution Path

Instead of modifying more code, the auction completion workflow was traced step by step.

The execution path is:

Auction Ends
      │
      ▼
Determine Winner
      │
      ▼
Fire Winner Event
      │
      ▼
Transaction Manager
      │
      ▼
Create Transaction
      │
      ▼
Create External Provider
      │
      ▼
Escrow API

Since the Transaction Manager never received control, the investigation moved further upstream.


Reviewing the Bid Manager

The winner determination logic resides inside the Bid Manager.

The following event was confirmed to exist:

do_action(
    'flipnzee_auction_winner_determined',
    $auction_id,
    $winner
);

The event itself was not missing.

Instead, attention shifted to the code responsible for deciding whether a winner should be declared.


Problems Identified

During inspection, the reserve price validation logic had become increasingly difficult to follow after several previous feature additions.

Several architectural issues were identified.

Mixed Responsibilities

The reserve price helper was no longer acting as a simple validation function.

Instead, it contained:

  • Database queries
  • Activity logging
  • Winner modification
  • Business rules
  • Validation logic

A helper function should ideally perform only one task.


Recursive Logic

The helper contained recursive calls back into itself.

This unnecessarily complicated the control flow and made debugging much harder.


Inconsistent Parameters

Different parts of the code expected different inputs.

Some calls passed:

Auction ID

while the helper expected:

Auction Object

This inconsistency made the workflow fragile and difficult to reason about.


Duplicate Business Rules

Reserve price validation appeared in multiple locations.

When business rules are duplicated:

  • bugs become harder to fix,
  • future changes become risky,
  • behavior can become inconsistent.

A single source of truth is always preferable.


Why This Matters

The transaction system depends entirely on the auction lifecycle.

If the winner determination process is unstable, then:

  • transactions cannot be created,
  • provider records cannot be generated,
  • Escrow integration cannot begin.

Rather than continuing to build on uncertain foundations, the focus shifted toward stabilizing the auction lifecycle first.


Architectural Principle

This lesson reinforced an important software engineering principle.

Each stage of the workflow should have one clearly defined responsibility.

Determine Winner
        │
        ▼
Validate Reserve Price
        │
        ▼
Declare Winner
        │
        ▼
Fire Event
        │
        ▼
Create Transaction

When each stage performs only one job, the entire workflow becomes easier to understand, test, and extend.


Benefits of the Refactor

Although this lesson does not introduce new user-facing functionality, it significantly improves the maintainability of the codebase.

Benefits include:

  • Cleaner control flow.
  • Easier debugging.
  • Reduced code duplication.
  • Better separation of concerns.
  • More predictable transaction lifecycle.
  • Stronger foundation for Escrow integration.

Looking Ahead

With the transaction architecture now largely complete and the root cause isolated to the winner determination workflow, the next phase will focus on simplifying the reserve price validation logic into a dedicated, single-purpose component.

Once the auction lifecycle is fully stabilized, the transaction manager, external provider manager, and Escrow integration will operate on a much more reliable foundation.


Lesson 134 demonstrates that effective debugging is often about validating assumptions rather than immediately writing new code. By tracing the complete execution path and identifying weaknesses in the winner determination workflow, Flipnzee Auctions moves closer to a robust, maintainable architecture capable of supporting future payment providers and marketplace features.

Lesson 133: Refactoring the External Provider Manager

As Flipnzee Auctions continued to evolve, it became clear that the External Provider Manager was beginning to take on too many responsibilities. Earlier implementations mixed database operations, provider selection, and external API communication inside a single class. While functional, this made the code difficult to extend and harder to maintain.

In this lesson, the architecture was refactored so that each component has a single, well-defined responsibility. Although no new user-facing functionality was added, this refactoring lays the foundation for future integrations with Escrow.com and other external transaction providers.


Why This Refactor Was Needed

The original implementation blurred several different responsibilities:

  • Creating local provider records.
  • Communicating with external APIs.
  • Updating provider metadata.
  • Managing provider lifecycle.

As the Escrow integration matured, it became apparent that separating these concerns would produce cleaner, more maintainable code.

The objective of this lesson was not to change functionality, but to improve the plugin architecture.


New Responsibilities

The transaction workflow is now organized into distinct layers.

Transaction Manager
        │
        ▼
External Provider Manager
        │
        ▼
Escrow API Client
        │
        ▼
Escrow.com

Each layer now performs only one job.

Transaction Manager

Responsible for:

  • Creating internal transactions.
  • Creating local provider records.
  • Building canonical transaction payloads.
  • Coordinating provider synchronization.

External Provider Manager

Responsible for:

  • Managing provider database records.
  • Delegating API requests to the appropriate provider client.
  • Synchronizing provider metadata.

It no longer performs HTTP requests directly.

Escrow API Client

Responsible for:

  • Payload validation.
  • API communication.
  • Response normalization.
  • Returning a standardized result to the application.

Provider Record Lifecycle

When a transaction is created, Flipnzee now creates an associated provider record before contacting the external provider.

The lifecycle is:

Create Transaction
        │
        ▼
Create Provider Record
        │
        ▼
Call Escrow API
        │
        ▼
Receive Response
        │
        ▼
Update Provider Record

This approach ensures every external transaction can be tracked independently from the auction transaction itself.


New Provider Synchronization

A new update_provider() method was introduced to synchronize provider information after receiving a successful response from the external provider.

Typical fields include:

  • Provider reference
  • Provider URL
  • Current provider status
  • Updated timestamp

This keeps the local database synchronized with the external provider without coupling database logic to the API client.


Improved Logging

Additional logging was added throughout the provider lifecycle.

Examples include:

  • Provider record creation
  • Provider synchronization
  • Failed provider updates
  • Database errors

These logs make debugging significantly easier during development and future integrations.


Cleaner Separation of Concerns

One of the biggest improvements introduced in this lesson is architectural rather than functional.

Instead of one large class handling everything, each class now has a clearly defined responsibility.

This makes it easier to:

  • Add new payment providers.
  • Replace existing providers.
  • Unit test components individually.
  • Extend the plugin without affecting unrelated functionality.

Current Status

While the External Provider Manager refactoring is now largely complete, testing also revealed that parts of the auction winner determination workflow require additional cleanup before the full transaction pipeline can be considered production-ready.

In particular, the reserve price validation logic inside the Bid Manager has accumulated duplicate and inconsistent code during previous iterations. Rather than layering additional features on top of unstable logic, the next lesson will focus on simplifying and stabilizing the winner determination process before continuing with further provider synchronization enhancements.

This is a good example of how software engineering often involves improving existing architecture before introducing new functionality. Careful refactoring at the right time helps keep a growing project maintainable and reduces the likelihood of subtle bugs appearing later as new features are added.


Lesson 133 demonstrates an important software engineering principle: clean architecture is an investment. By separating provider management, transaction orchestration, and external API communication into independent components, Flipnzee Auctions becomes easier to maintain today and significantly easier to extend in the future.

Lesson 133: Persisting Provider References and Synchronizing Provider Status

With the transaction payload standardized in Lesson 132, the Flipnzee Auctions plugin now has a consistent way to exchange transaction data between its internal components. The next step is ensuring that information returned by external providers is not lost.

Creating an Escrow transaction is only half of the process. Once the provider responds, the plugin should store the provider’s transaction reference, record its current status, and keep the local database synchronized with the external service.

Lesson 133 focuses on completing that connection.


Why this lesson is important

Until now, the transaction workflow has looked like this:

Auction Closed
      │
      ▼
Local Transaction Created
      │
      ▼
External Provider Record Created
      │
      ▼
Escrow API Request
      │
      ▼
Response Returned

Although the API returns useful information, much of it is not yet persisted for future use.

Without storing provider references, the plugin cannot reliably:

  • Revisit an external transaction
  • Check its latest status
  • Display provider information in the admin area
  • Recover gracefully after temporary API failures

The Goal

After this lesson, every successful provider transaction should immediately update the corresponding provider record.

The workflow becomes:

Auction Closed
      │
      ▼
Local Transaction
      │
      ▼
Create Provider Record
      │
      ▼
Escrow Transaction
      │
      ▼
Store Provider Reference
      │
      ▼
Update Provider Status
      │
      ▼
Future Synchronization

The provider record becomes the permanent link between Flipnzee Auctions and the external provider.


Provider Information to Store

When a provider successfully creates a transaction, the plugin should save information such as:

  • Provider transaction reference
  • Current provider status
  • Provider transaction URL (when available)
  • Last updated timestamp
  • Synchronization notes

Persisting this information ensures that future API calls always know which external transaction they belong to.


Synchronizing Status

Rather than leaving every provider record in a generic “Pending” state, the plugin will begin recording the actual status returned by the provider.

Typical values may include:

  • Created
  • Awaiting Payment
  • Payment Received
  • In Progress
  • Completed
  • Cancelled

Using normalized status values makes the rest of the plugin independent of provider-specific terminology.


Strengthening the External Provider Manager

The External Provider Manager now evolves from simply forwarding API requests into coordinating provider lifecycle management.

Its responsibilities include:

  • Sending provider requests
  • Validating provider responses
  • Saving provider references
  • Updating provider status
  • Returning standardized results to the Transaction Manager

This keeps provider-specific behavior isolated from the rest of the application.


Benefits

Persistent Transaction Tracking

Every auction remains permanently linked to its external provider transaction.

Better Administration

Administrators can identify provider transactions without manually searching the external platform.

Improved Reliability

If synchronization fails, the stored provider reference allows the plugin to retry later.

Foundation for Scheduled Synchronization

Saving provider identifiers prepares the plugin for future background status checks using WP-Cron.

Webhook Ready

Future webhook events can immediately identify the correct local transaction because the provider reference has already been stored.


Architecture After Lesson 133

Auction Closed
      │
      ▼
Transaction Manager
      │
      ▼
Canonical Transaction Payload
      │
      ▼
External Provider Manager
      │
      ▼
Escrow API Client
      │
      ▼
Persist Provider Reference
      │
      ▼
Synchronize Provider Status
      │
      ▼
Local Database

This completes the core transaction lifecycle by ensuring that local records remain connected to their corresponding external transactions.


What We Will Implement

During this lesson we will:

  • Process successful responses returned by the Escrow API client.
  • Persist provider transaction references in the database.
  • Update provider status automatically after transaction creation.
  • Store provider URLs when available.
  • Record synchronization timestamps.
  • Improve activity logging for provider creation and status updates.
  • Prepare the architecture for future scheduled synchronization and webhook support.

What You’ll Learn

By completing Lesson 133, you’ll gain practical experience with:

  • Synchronizing local records with external services.
  • Designing reliable provider integrations.
  • Persisting external identifiers for long-term tracking.
  • Building extensible transaction workflows.
  • Preparing a WordPress plugin for production-grade third-party integrations.

Next Lesson

Lesson 134 will introduce an External Provider Management screen within the WordPress admin area, allowing administrators to view provider records, monitor synchronization status, inspect provider references, and manage external transactions from a single dashboard.