Lesson 132 Implementation: Standardizing the Transaction Payload

As the Flipnzee Auctions plugin continued to evolve, one architectural issue became increasingly apparent. Although the Transaction Manager, External Provider Manager, and Escrow API Client all worked together, each component constructed or interpreted transaction data slightly differently.

This lesson introduces a significant refactoring by defining a canonical transaction payload that is shared across the entire Escrow integration workflow.

Rather than rebuilding transaction data at each layer, a single standardized payload is now created and passed unchanged throughout the transaction lifecycle.


Why this refactoring was necessary

Prior to Lesson 132, each component handled transaction information independently.

The Transaction Manager assembled transaction details before invoking the External Provider Manager. The Provider Manager then rebuilt another payload before sending it to the Escrow API Client. Finally, the API Client performed its own validation of required fields.

Although functional, this approach resulted in duplicated logic and increased the risk of inconsistencies whenever transaction fields changed.

The architecture previously resembled:

Transaction Manager
        │
        ▼
Creates Payload A
        │
        ▼
External Provider Manager
        │
        ▼
Creates Payload B
        │
        ▼
Escrow API Client

Every translation introduced another opportunity for errors.


Building a Canonical Transaction Payload

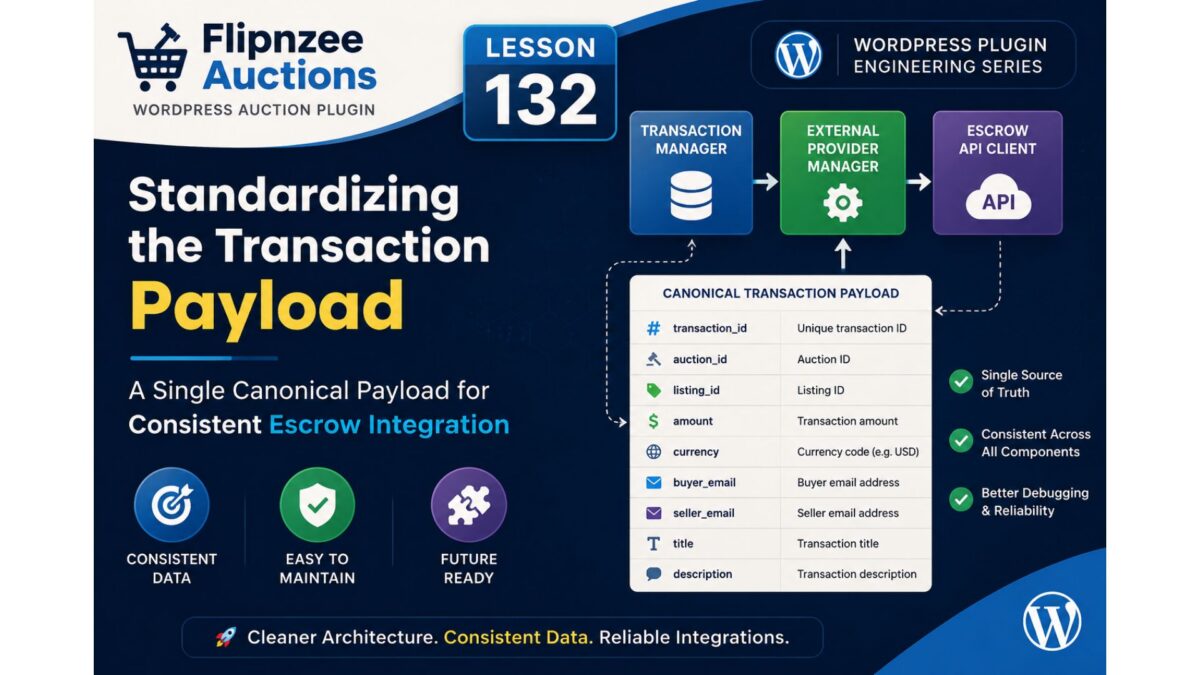
Lesson 132 establishes the Transaction Manager as the single source of truth for transaction data.

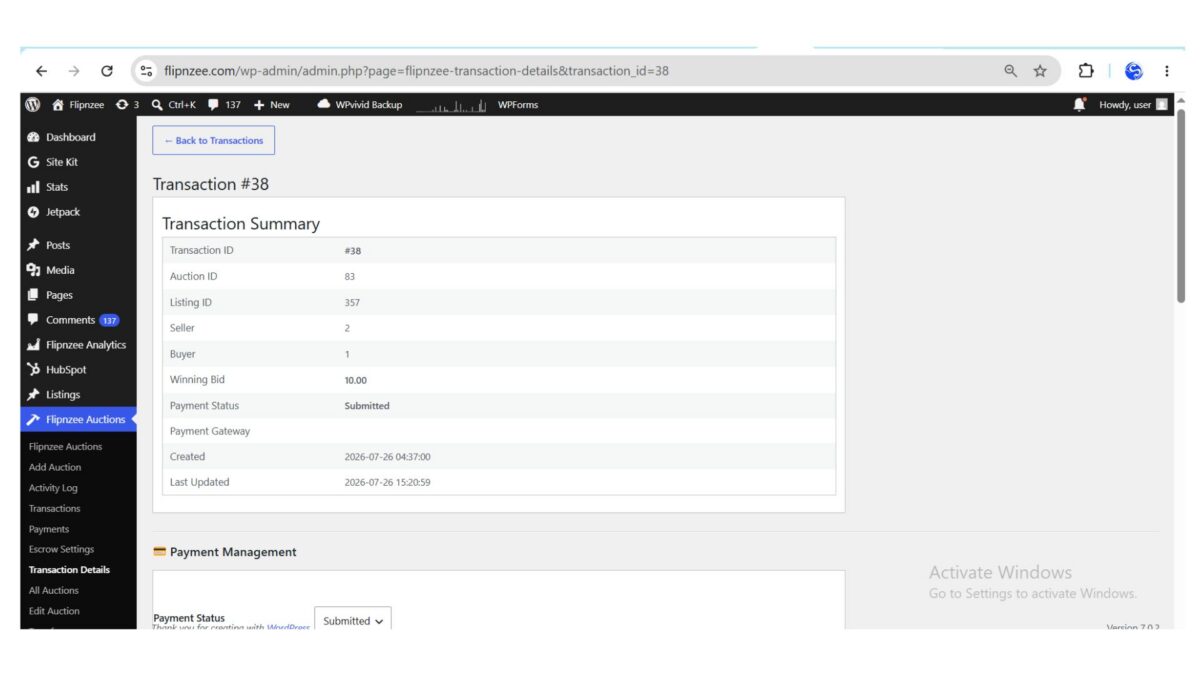
A complete transaction payload is now created immediately after the local transaction record is generated.

The payload includes:

  • Transaction ID
  • Auction ID
  • Listing ID
  • Winning amount
  • Currency
  • Buyer ID
  • Seller ID
  • Buyer email
  • Seller email
  • Transaction title
  • Description

Instead of reconstructing missing values later, all required information now travels together through the integration.


Simplifying the External Provider Manager

The External Provider Manager has been refactored into a validation and routing layer.

Rather than generating missing transaction fields, it now performs two responsibilities:

  • Validate the incoming payload.
  • Pass the standardized payload directly to the Escrow API Client.

This significantly reduces duplicated business logic while making the provider layer much easier to maintain.


Improved API Validation

The Escrow API Client now validates the canonical payload before attempting any API communication.

Required fields are checked consistently, allowing missing or invalid data to be detected immediately before an HTTP request is made.

This results in clearer error reporting and a more predictable transaction workflow.


Architectural Improvements

The transaction flow is now much simpler.

Before

Auction Closed
      │
      ▼
Transaction Manager
      │
      ▼
Creates Custom Payload
      │
      ▼
External Provider Manager
      │
      ▼
Creates Another Payload
      │
      ▼
Escrow API Client

After

Auction Closed
      │
      ▼
Transaction Manager
      │
      ▼
Canonical Transaction Payload
      │
      ▼
External Provider Manager
      │
      ▼
Escrow API Client
      │
      ▼
Simulation / Sandbox / Production

Every component now communicates using the same data contract.


Benefits

This refactoring provides several long-term advantages.

Single Source of Truth

Transaction information is created once and reused throughout the integration.

Reduced Code Duplication

Provider-specific classes no longer recreate values that already exist.

Easier Debugging

Developers can inspect a single payload throughout the transaction lifecycle instead of tracing multiple array transformations.

Better Maintainability

Adding or modifying transaction fields now requires changes in only one location.

Future Provider Support

Additional payment providers can consume the same standardized payload without requiring custom payload builders.


Current Status

With Lesson 132 complete, the Escrow integration architecture has become considerably cleaner.

The plugin now consists of clearly separated responsibilities:

  • Transaction Manager
  • External Provider Manager
  • Escrow API Client
  • Canonical Transaction Payload
  • Simulation, Sandbox, and Production environments

This standardized data contract lays a solid foundation for future provider integrations while reducing complexity across the transaction workflow.

https://github.com/SplendidDigital/flipnzee-auctions/releases/tag/lesson-132-stable


Next Lesson

Lesson 133 will focus on persisting provider references and synchronizing provider status. The plugin will begin storing external transaction identifiers returned by Escrow.com and updating local provider records with the latest status, preparing the system for ongoing synchronization and future webhook support.

Lesson 132: Standardizing the Transaction Payload Across the Escrow Integration
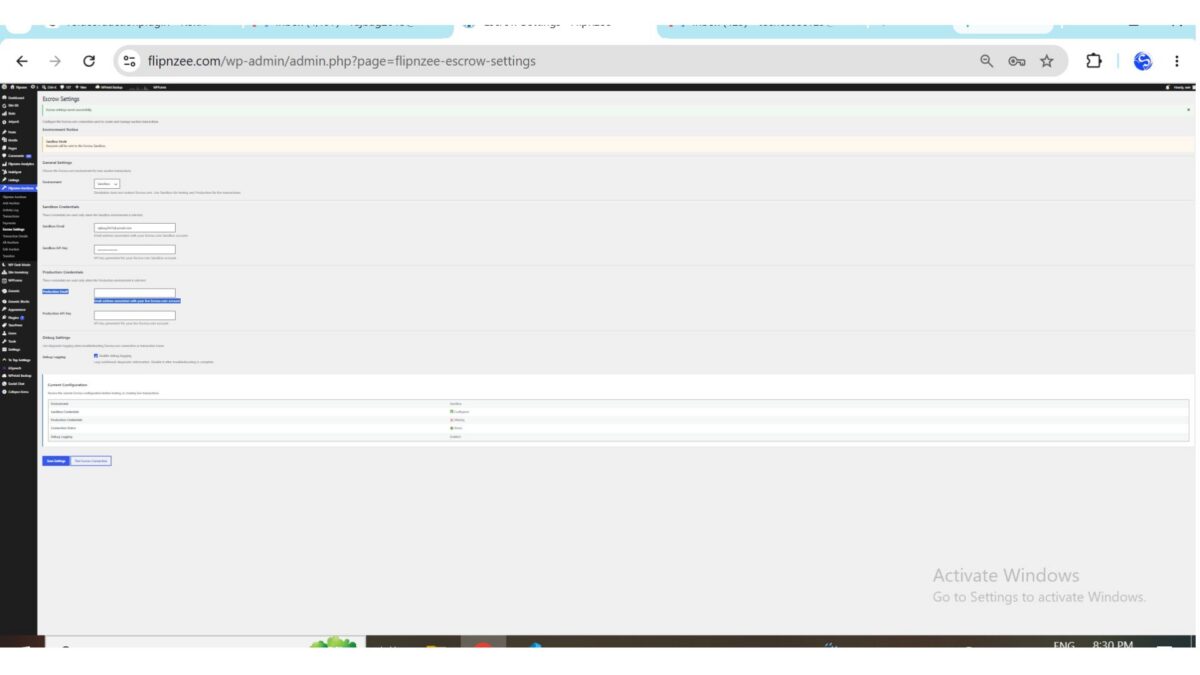
In the previous lesson, the External Provider Manager was introduced as an abstraction layer between the Flipnzee Auctions plugin and external payment providers. This significantly improved the architecture by separating transaction management from provider-specific logic.

During testing, however, another issue became apparent. Different components were building and consuming transaction data in slightly different formats. While the Transaction Manager, External Provider Manager, and Escrow API Client all exchanged arrays of data, they did not always agree on which fields should exist or what they should be called.

Lesson 132 focuses on solving this problem by introducing a canonical transaction payload.


The Problem

Prior to this lesson, each component expected slightly different data.

For example:

  • Transaction Manager created transaction information.
  • External Provider Manager rebuilt parts of the payload.
  • Escrow API Client validated fields independently.

Although this worked in simple scenarios, it made debugging difficult because each layer could modify or recreate the transaction data.

The architecture looked like this:

Transaction Manager
        │
        ▼
Creates custom payload
        │
        ▼
External Provider Manager
        │
        ▼
Creates another payload
        │
        ▼
Escrow API Client

Every translation introduced another opportunity for inconsistencies.


The Solution

Lesson 132 introduces a single canonical payload structure that travels unchanged through the Escrow integration.

Instead of rebuilding arrays multiple times, the Transaction Manager becomes the authoritative source of transaction data.

The new workflow becomes:

Transaction Manager
        │
        ▼
Canonical Transaction Payload
        │
        ▼
External Provider Manager
        │
        ▼
Escrow API Client

Every component now speaks the same language.


Canonical Payload

The standardized transaction payload contains all information required by the provider layer.

Typical fields include:

  • Transaction ID
  • Auction ID
  • Listing ID
  • Amount
  • Currency
  • Buyer email
  • Seller email
  • Title
  • Description

Rather than generating missing values later, these are prepared once and reused throughout the transaction lifecycle.


Benefits

Single Source of Truth

Transaction information is generated once and remains consistent throughout the workflow.


Easier Debugging

When an API request fails, developers can inspect one payload instead of tracing multiple array transformations across different classes.


Reduced Code Duplication

Provider managers no longer recreate values already available from the Transaction Manager.


Better Maintainability

Future changes to transaction fields require updates in only one location instead of several independent methods.


Improved Extensibility

Additional payment providers can consume the same payload without requiring provider-specific transaction builders.

This makes future integrations significantly easier.


Architectural Improvement

The transaction flow is now much cleaner.

Before:

Transaction Manager
        │
        ▼
Creates Payload A
        │
        ▼
External Provider Manager
        │
        ▼
Creates Payload B
        │
        ▼
Escrow API Client

After:

Transaction Manager
        │
        ▼
Canonical Transaction Payload
        │
        ▼
External Provider Manager
        │
        ▼
Escrow API Client

This removes unnecessary translation layers while making the integration easier to understand.


What We Will Implement

During this lesson we will:

  • Define the canonical transaction payload.
  • Refactor the Transaction Manager to construct the payload once.
  • Remove duplicate payload construction from the External Provider Manager.
  • Ensure the Escrow API Client consumes the standardized structure directly.
  • Improve logging so the same payload can be traced throughout the entire transaction lifecycle.

What We’ll Learn

By the end of Lesson 132, you will understand:

  • Why a canonical data structure simplifies software architecture.
  • How to reduce coupling between components.
  • How consistent data contracts improve debugging and maintenance.
  • Why production-quality plugins rely on standardized payloads rather than ad hoc arrays.

Next Lesson

Lesson 133 will focus on persisting Escrow provider references and synchronizing provider status with local transactions, allowing the plugin to track external transaction identifiers and keep local records aligned with the provider throughout the transaction lifecycle.

Lesson 131 Implementation: Introducing the External Provider Manager

In the previous lessons, the Escrow API client was refactored into a reusable HTTP client capable of communicating with Escrow.com in Simulation, Sandbox, and Production environments. While this significantly improved the networking layer, the rest of the plugin still interacted directly with the Escrow client.

This lesson introduces an important architectural improvement: the External Provider Manager.

Rather than allowing business logic to communicate directly with a specific payment provider, all external transaction providers are now accessed through a common manager. Although Escrow.com is currently the only supported provider, this abstraction makes the plugin easier to maintain and allows additional providers to be introduced in the future without affecting the transaction workflow.


Why this refactoring was needed

Prior to this lesson, various parts of the plugin were aware of the Escrow API client itself. That meant changing providers or supporting multiple providers would require modifications throughout the codebase.

The new architecture centralizes that responsibility.

Instead of:

Transaction Manager
        │
        ▼
Escrow API Client

the flow now becomes:

Transaction Manager
        │
        ▼
External Provider Manager
        │
        ▼
Escrow API Client

The Transaction Manager no longer needs to know how Escrow transactions are created. It simply requests that an external transaction be created using the configured provider.


What was implemented

Lesson 131 introduces the Flipnzee_External_Provider_Manager class as the single entry point for external transaction providers.

The manager now:

  • Accepts a provider identifier.
  • Validates the requested provider.
  • Creates an Escrow API client when required.
  • Converts internal transaction data into an Escrow-compatible payload.
  • Returns a standardized response to the calling code.

This keeps provider-specific logic isolated from the rest of the plugin.


Escrow payload builder

A dedicated payload builder was added to translate Flipnzee transaction data into the format expected by the Escrow API client.

Typical information included in the payload includes:

  • Transaction title
  • Description
  • Amount
  • Currency
  • Buyer email
  • Seller email

Keeping this translation in one place makes future API changes much easier to accommodate.


Standardized provider responses

The Provider Manager also ensures callers always receive a consistent response structure.

Whether the request succeeds or fails, the calling code receives a predictable array describing:

  • Success or failure
  • Message
  • Provider response

This avoids provider-specific handling throughout the plugin.


Benefits

This refactoring provides several long-term advantages.

Separation of responsibilities

The Transaction Manager no longer performs provider-specific work.

Improved maintainability

Changes to Escrow integration are now isolated within the provider layer.

Easier testing

Simulation Mode, Sandbox, and Production all continue to function without requiring changes elsewhere in the plugin.

Future extensibility

Supporting additional transaction providers becomes significantly easier because the Transaction Manager communicates only with the Provider Manager rather than individual provider implementations.

Potential future providers could include:

  • Escrow.com
  • Trustap
  • Stripe Connect
  • Manual escrow workflows
  • Additional marketplace services

Current status

At the end of Lesson 131, the overall architecture has matured considerably.

The plugin now consists of:

  • Transaction Manager
  • External Provider Manager
  • Escrow Provider
  • Refactored Escrow API Client
  • Simulation, Sandbox, and Production environments

While additional work remains before production-ready Escrow integration is complete, the major architectural foundation is now in place.


Next lesson

Lesson 132 will focus on standardizing the transaction payload shared between the Transaction Manager, External Provider Manager, and Escrow API Client. Establishing a single canonical payload will simplify debugging, eliminate duplicated mapping logic, and prepare the integration for reliable end-to-end transaction processing.

Lesson 131 – Creating the First Real Escrow Transaction

Over the previous lessons, we’ve focused on building a reliable foundation for the Escrow integration within Flipnzee Auctions. We’ve introduced environment management, refactored the API client, standardized response handling, and built a production-ready administration interface.

Although the plugin is now capable of communicating with Escrow.com, it still isn’t performing the task it was ultimately designed for—creating real Escrow transactions.

In this lesson, that changes.

We’ll implement the first step of the complete Escrow transaction lifecycle by creating an actual Escrow transaction through the refactored API client.


Where We Stand

At the end of Lesson 130, the plugin supports:

  • Simulation environment
  • Sandbox environment
  • Production environment
  • Credential validation
  • Connection testing
  • Standardized API responses
  • Configuration dashboard

The networking layer is complete enough to begin sending real business requests.


The Missing Piece

Winning an auction currently updates the local database.

The plugin knows:

  • the winning bidder,
  • the auction,
  • the final price,
  • the payment provider.

However, nothing is yet created at Escrow.com.

The workflow still ends inside WordPress.


Current Workflow

Today’s workflow looks like this:

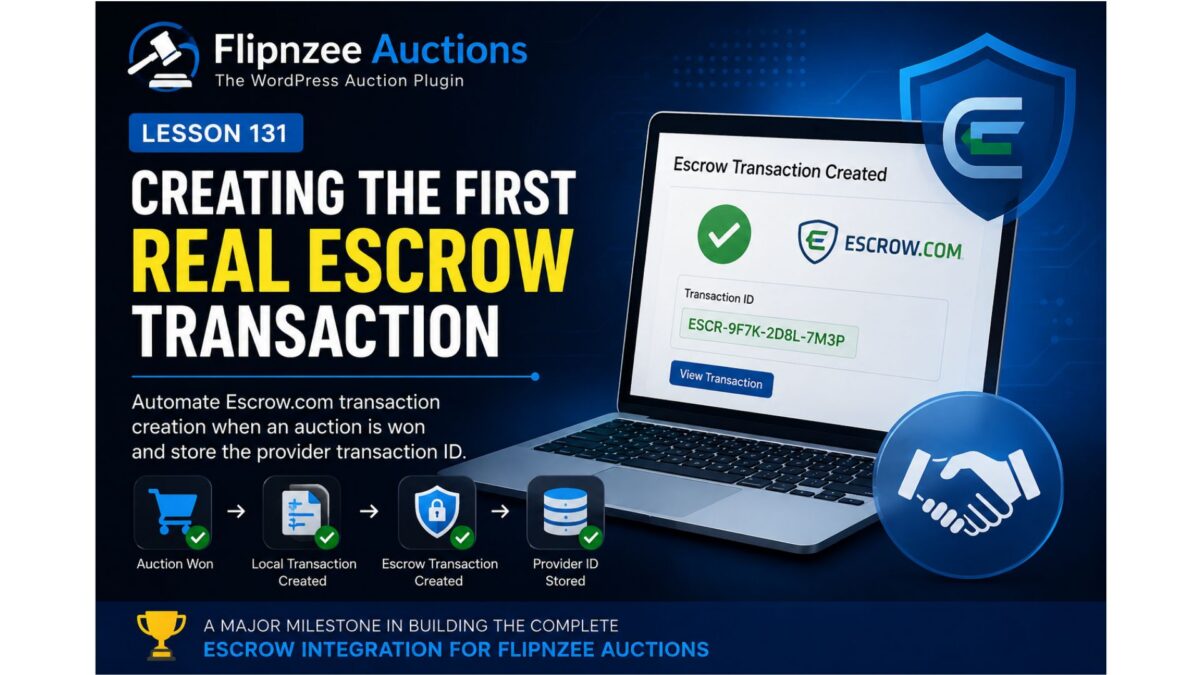
Auction Ends
        │
        ▼
Winner Selected
        │
        ▼
Local Transaction Created
        │
        ▼
END

While useful, this means the administrator must manually create an Escrow transaction.

That defeats the purpose of integrating directly with Escrow.com.


New Workflow

After Lesson 131, the process becomes significantly more powerful.

Auction Ends
        │
        ▼
Winner Selected
        │
        ▼
Local Transaction Created
        │
        ▼
Escrow Transaction Created
        │
        ▼
Provider Transaction ID Stored

This becomes the beginning of the complete payment lifecycle.


Objectives

The primary objective of this lesson is to automate the creation of an Escrow transaction whenever the plugin is ready to initiate payment.

By the end of this lesson, Flipnzee Auctions will be capable of requesting a new transaction from Escrow.com using the existing API client.


Building on Existing Architecture

One advantage of the previous refactoring work is that almost everything required already exists.

The plugin already provides:

  • Escrow API Client
  • External Provider Manager
  • Transaction Manager
  • Standardized responses
  • Environment management

Rather than introducing a completely new architecture, this lesson simply connects these existing components together.


Transaction Creation

The Escrow API client already understands how to communicate with the selected environment.

We’ll now extend it with support for creating transactions.

The request will include information such as:

  • auction identifier,
  • transaction amount,
  • buyer,
  • seller,
  • currency,
  • description.

Initially, the request will focus on the minimum data required to establish the transaction.

Additional metadata can be added in future lessons.


Provider Transaction IDs

One of the most important pieces of information returned by Escrow.com is its transaction identifier.

This identifier becomes the permanent link between:

  • Flipnzee Auctions
  • Escrow.com

Rather than relying solely on local transaction IDs, the plugin will now store the provider’s unique identifier for future synchronization.


Centralized Workflow

Instead of allowing different parts of the plugin to communicate directly with Escrow.com, all requests will continue flowing through the Escrow API client.

The architecture remains:

Auction
      │
      ▼
Transaction Manager
      │
      ▼
External Provider Manager
      │
      ▼
Escrow API Client
      │
      ▼
Escrow.com

Maintaining this separation keeps networking concerns isolated from business logic.


Error Handling

Creating an external transaction introduces new failure scenarios.

Examples include:

  • network failures,
  • authentication errors,
  • invalid request data,
  • temporary provider outages.

Rather than assuming success, the plugin will continue using the standardized response format introduced in earlier lessons.

This ensures consistent error handling throughout the integration.


Preparing for Synchronization

Creating the transaction is only the beginning.

Future lessons will build upon the provider transaction identifier to support:

  • transaction synchronization,
  • status updates,
  • payment completion,
  • cancellations,
  • dispute handling,
  • webhook processing.

Lesson 131 establishes the foundation upon which these features will be built.


Expected Outcome

After completing this lesson, Flipnzee Auctions will no longer stop after creating a local transaction.

Instead, it will immediately communicate with the configured Escrow environment and request creation of a corresponding provider transaction.

The resulting provider identifier will be stored locally, allowing future synchronization with Escrow.com.


Conclusion

Configuration alone does not create business value. Real value begins when software starts automating real-world workflows.

Lesson 131 represents one of the most significant milestones in the Flipnzee Auctions project. For the first time, the plugin moves beyond configuration and local transaction management to begin interacting directly with Escrow.com as part of the auction lifecycle.

In the next implementation lesson, we’ll connect the auction workflow to the Escrow API client, create our first provider transaction, and persist the returned transaction identifier for future synchronization.

Lesson 130 – Validating Escrow Credentials and Strengthening Environment Safety

Over the past several lessons, we’ve steadily improved the architecture of the Escrow integration within Flipnzee Auctions. The API client now relies on the WordPress HTTP API, networking has been centralized, and response handling has been standardized.

While these improvements make the client easier to maintain, production-ready software requires more than clean code. It must also protect administrators from configuration mistakes before they affect live transactions.

In this lesson, we’ll improve how the plugin validates Escrow credentials and handles environment-specific configuration.


Where We Stand

The Escrow Settings page currently supports:

  • Simulation mode
  • Sandbox mode
  • Production mode
  • Sandbox credentials
  • Production credentials
  • Connection testing
  • Debug logging

The API client can communicate with different environments while returning standardized responses throughout the plugin.

Although this provides a solid foundation, the plugin still assumes that administrators have entered valid credentials.


Why Validation Matters

Incorrect configuration is one of the most common causes of integration failures.

Examples include:

  • selecting Sandbox without entering Sandbox credentials,
  • selecting Production while leaving production credentials empty,
  • accidentally using Sandbox credentials in Production,
  • forgetting to save updated API keys.

Without validation, these mistakes are only discovered after a connection attempt has already failed.

A better administrator experience is to identify these problems before any HTTP request is sent.


Objectives of Lesson 130

The goal of this lesson is to introduce stronger validation and safer environment handling throughout the Escrow integration.

By the end of this lesson, the plugin will perform additional checks before attempting to communicate with Escrow.com.


Credential Validation

The settings page will verify that the required credentials exist for the currently selected environment.

For example:

Simulation

No credentials are required.

Simulation mode remains available for plugin development without requiring an Escrow account.


Sandbox

The plugin will verify that:

  • Sandbox Email has been provided.
  • Sandbox API Key has been provided.

If either value is missing, administrators will receive a clear validation message.


Production

Likewise, the plugin will verify that:

  • Production Email has been configured.
  • Production API Key has been configured.

This prevents unnecessary API requests that are guaranteed to fail.


Safer Environment Handling

We’ll also improve how environments are interpreted throughout the plugin.

Instead of relying solely on user input, the Escrow client will explicitly determine which credentials belong to the currently selected environment.

This makes the code easier to understand while reducing the possibility of accidentally using the wrong credentials.


Improved Administrator Feedback

Validation messages should explain exactly what needs attention.

Rather than displaying generic failures, administrators should immediately understand:

  • which environment is active,
  • which credentials are missing,
  • why a connection test could not proceed.

Clear feedback reduces troubleshooting time and improves the overall configuration experience.


Defensive Programming

This lesson also introduces another important software engineering principle: defensive programming.

Instead of assuming that configuration is always correct, the plugin will verify its assumptions before performing external operations.

This approach makes integrations more reliable while reducing unexpected runtime failures.


Preparing for Live Transactions

As Flipnzee Auctions moves closer to supporting real Escrow.com transactions, preventing configuration mistakes becomes increasingly important.

By validating credentials before communicating with the API, we’re building a safer foundation for future lessons involving live transaction creation, synchronization, and payment processing.


Expected Outcome

After completing this lesson, the Escrow integration will perform environment-aware credential validation before initiating external communication.

Administrators will receive clearer feedback when configuration is incomplete, while the API client will become more resilient against invalid settings.

These improvements enhance both usability and reliability without changing the public interface of the Escrow API client.


Conclusion

A robust integration is not defined solely by its ability to communicate with external services—it must also guide administrators toward correct configuration and prevent avoidable mistakes.

By introducing stronger credential validation and safer environment handling, we’re taking another step toward making Flipnzee Auctions a production-quality WordPress plugin capable of supporting real-world website transactions with confidence.

In the next lesson, we’ll implement these improvements by adding environment-aware validation, clearer administrator notices, and additional safety checks before any Escrow API request is made.

Lesson 130 – Building a Production-Ready Escrow Settings Interface

In the previous lessons, we focused on strengthening the internal architecture of the Escrow integration. The API client was refactored to use the WordPress HTTP API, response handling became standardized, and the plugin gained support for Simulation, Sandbox, and Production environments.

While these backend improvements significantly improved maintainability, the administrator experience still had room for improvement.

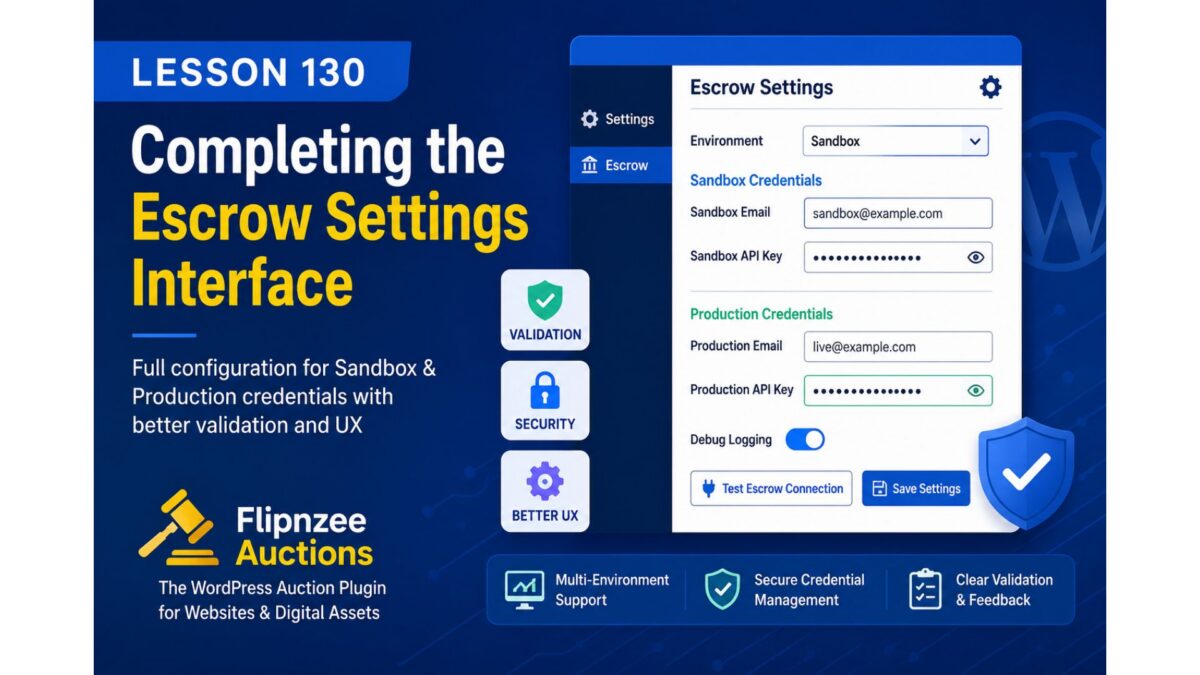
In this lesson, we’ll redesign the Escrow Settings page to provide a cleaner interface, better validation, and a clearer overview of the plugin’s configuration.


Where We Left Off

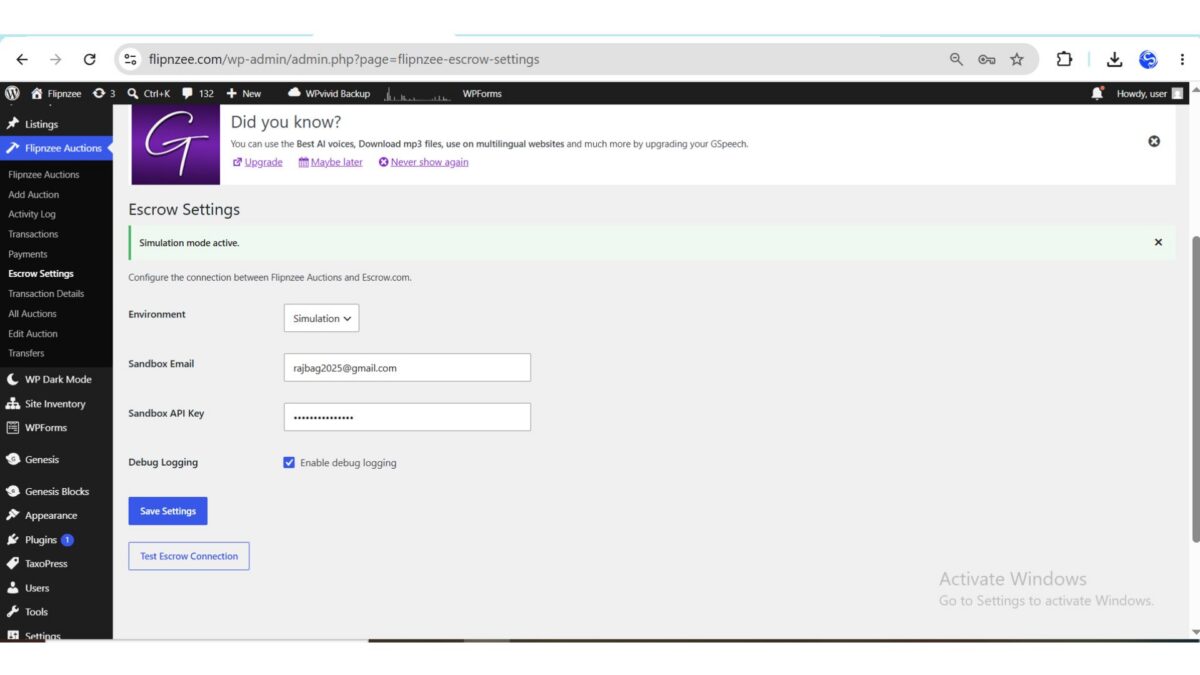
At the end of Lesson 129, administrators could configure the Escrow integration, but the page was fairly minimal.

It provided:

  • Environment selection
  • Sandbox credentials
  • Debug logging
  • Connection testing

Although functional, it didn’t fully expose the capabilities already built into the Escrow API client.


Objectives

The goal of this lesson is to transform the Escrow Settings page into a more polished administration interface while keeping the existing backend architecture intact.

The improvements focus on usability rather than introducing new API functionality.


Introducing Multiple Configuration Sections

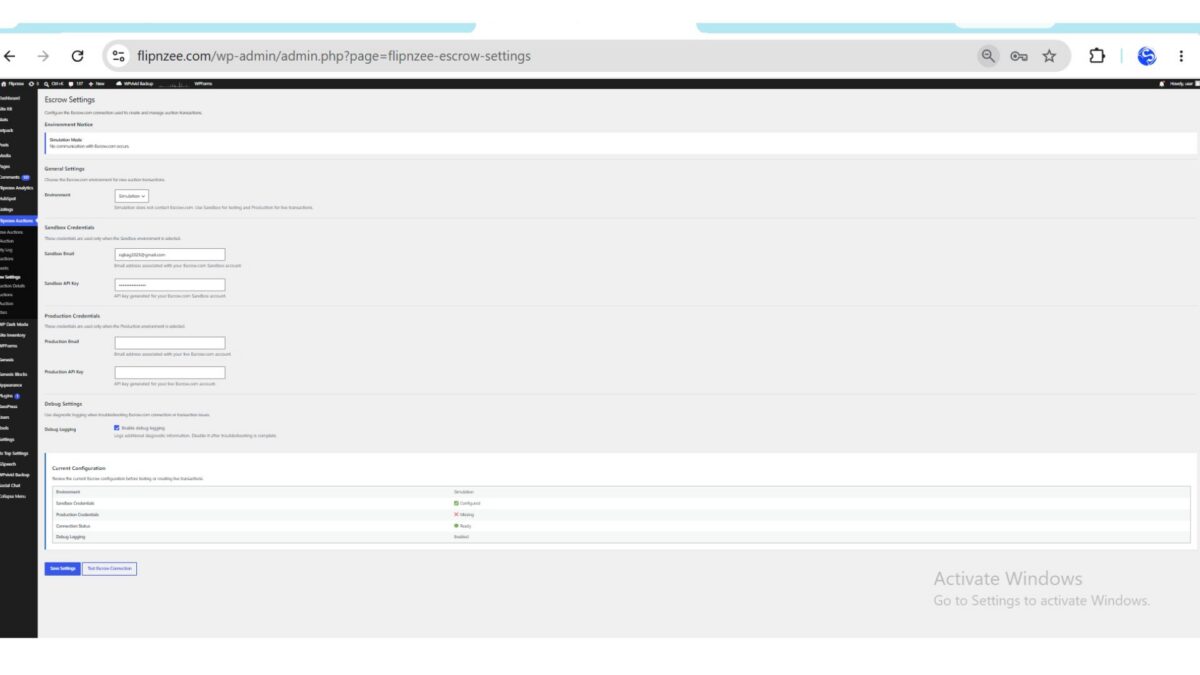
Instead of presenting every option inside a single table, the settings page is now divided into logical sections.

The new layout includes:

  • Environment Notice
  • General Settings
  • Sandbox Credentials
  • Production Credentials
  • Debug Settings
  • Current Configuration

Breaking the page into smaller sections makes navigation easier and improves readability as the plugin continues to grow.


Environment Awareness

One of the most noticeable improvements is the addition of an environment notice.

Whenever an administrator selects an environment, the page immediately explains what that environment represents.

For example:

  • Simulation performs no external requests.
  • Sandbox communicates with the Escrow testing environment.
  • Production is intended for real Escrow transactions.

Providing this information directly within the interface reduces configuration mistakes and makes the plugin easier to understand.


Production Credentials

Previous versions of the settings page focused primarily on Sandbox credentials.

Lesson 130 introduces dedicated fields for live Escrow.com credentials.

Administrators can now configure:

  • Production Email
  • Production API Key

This completes the configuration interface and aligns it with the capabilities already implemented within the Escrow API client.


Better Input Validation

The plugin now validates configuration before saving.

Depending on the selected environment, administrators must provide the required credentials.

For example:

Sandbox mode requires:

  • Sandbox Email
  • Sandbox API Key

Production mode requires:

  • Production Email
  • Production API Key

Instead of saving incomplete settings, the plugin now displays clear validation messages, helping administrators resolve configuration problems before attempting to connect to Escrow.com.


Credential Verification

A small helper method now determines whether the required credentials exist for the active environment.

Rather than repeating this logic throughout the codebase, it has been centralized into a reusable method.

This helper is now used to determine whether the current configuration is ready for testing.


Smarter Connection Testing

One subtle but useful improvement is the Test Escrow Connection button.

Rather than allowing administrators to submit a request that is guaranteed to fail, the button now becomes unavailable whenever the required credentials are missing.

This defensive approach improves the overall user experience while reducing unnecessary API requests.


Configuration Dashboard

The settings page now concludes with a configuration summary.

Rather than forcing administrators to review multiple input fields, the dashboard provides a quick overview of the current Escrow configuration.

Information displayed includes:

  • Current Environment
  • Sandbox Credential Status
  • Production Credential Status
  • Connection Readiness
  • Debug Logging Status

This makes it much easier to verify the plugin’s configuration at a glance.


Cleaner Code Structure

Although the visual changes are significant, the internal architecture has also improved.

Several responsibilities have been moved into dedicated helper methods, including:

  • Environment labeling
  • Credential validation
  • Credential availability checks
  • Environment notices

This keeps the render_page() method focused on presentation while allowing reusable logic to remain centralized elsewhere in the class.


User Experience Improvements

Several smaller refinements were also introduced:

  • Better section headings
  • Improved field descriptions
  • More consistent spacing
  • Clearer labels
  • Improved accessibility through proper form labels
  • Better alignment with the native WordPress administration interface

While individually small, these improvements combine to create a much more polished configuration experience.


Preparing for Live Escrow Transactions

Although this lesson doesn’t yet create real Escrow transactions, it lays an important foundation for the lessons that follow.

Before a plugin can communicate reliably with an external payment provider, administrators must have confidence that their configuration is correct.

Lesson 130 ensures that the plugin can now validate and present that configuration much more effectively.


Expected Outcome

After completing this lesson, Flipnzee Auctions provides a significantly improved Escrow administration experience.

Administrators can:

  • Configure Sandbox and Production credentials separately.
  • Clearly identify the active environment.
  • Validate settings before saving.
  • Test only valid configurations.
  • Review their current configuration from a dedicated status dashboard.

These improvements make the plugin easier to configure, easier to troubleshoot, and better prepared for future production features.


Conclusion

As software matures, development gradually shifts from building core functionality to refining the overall user experience.

Lesson 130 demonstrates that production-ready software isn’t defined solely by powerful backend code. A well-designed administration interface is equally important, helping users configure the system correctly while reducing errors and simplifying maintenance.

With the configuration interface now significantly improved, the groundwork is complete for the next major milestone: creating and managing real Escrow.com transactions directly from Flipnzee Auctions.

In the next lesson, we’ll begin implementing the transaction lifecycle by initiating real Escrow transactions through the refactored API client, bringing the plugin one step closer to a fully production-ready Escrow integration.

https://github.com/SplendidDigital/flipnzee-auctions/releases/tag/lesson-130-stable

Lesson 129 – Simplifying Response Handling in the Escrow API Client

As Flipnzee Auctions continues to mature, one of the recurring goals is to reduce duplication while improving consistency across the codebase. After refactoring the Escrow API client in the previous lesson, we now have a centralized HTTP request layer built around the WordPress HTTP API.

Although that refactoring significantly improved the networking architecture, one area still contains unnecessary duplication: response construction.

In this lesson, we’ll simplify how the Escrow API client generates success and error responses.


Where We Left Off

Following the previous refactoring, every public method delegates its networking responsibilities to a reusable send_request() method.

The overall flow now looks like this:

Public Methods
        │
        ▼
send_request()
        │
        ▼
WordPress HTTP API
        │
        ▼
Escrow.com REST API

This removed duplicated networking logic and established a single entry point for all HTTP communication.

However, the responses returned by the client are still assembled in multiple places.


The Remaining Problem

Every interaction with the Escrow API ultimately returns a response array containing information such as:

  • success status
  • message
  • transaction reference
  • transaction status
  • endpoint
  • response code
  • response data

While these arrays follow the same general structure, they are still created repeatedly throughout the client.

This duplication increases maintenance effort because every future change requires modifying several return statements instead of one centralized implementation.


Objectives of Lesson 129

The goal of this lesson is to centralize response creation while keeping the public interface of the Escrow API client completely unchanged.

By the end of this lesson:

  • success responses will be generated consistently,
  • error responses will follow the same structure,
  • duplicated array construction will be removed,
  • networking code will become easier to read,
  • future enhancements will require fewer changes.

Separating Success and Error Responses

One useful design improvement is to clearly distinguish between successful operations and failed operations.

Rather than manually constructing response arrays throughout the client, we’ll introduce dedicated helper methods responsible for building standardized responses.

These helpers become the single source of truth for the response format used throughout the Escrow API client.


Benefits of Centralized Responses

Moving response construction into reusable helper methods provides several advantages.

Consistency

Every response—regardless of where it originates—shares the same structure.

This makes the client easier to consume throughout the plugin.


Maintainability

If new fields are added in the future, they only need to be implemented once.

For example, future enhancements might include:

  • request identifiers,
  • execution time,
  • timestamps,
  • provider metadata,
  • debugging information.

Instead of modifying numerous return statements, these additions can be made within a single helper.


Readability

The networking logic becomes easier to understand because it focuses solely on:

  • sending requests,
  • processing responses,
  • handling errors.

Constructing arrays is delegated to dedicated helper methods.

This separation makes the code significantly easier to follow.


Simulation Mode

Simulation mode remains an important part of the development workflow.

Rather than returning custom arrays directly, simulated responses will also use the new helper methods.

This ensures that simulation, sandbox, and production environments all produce responses with the same structure.

Maintaining identical response formats across environments simplifies testing and reduces the chance of environment-specific bugs.


Preparing for Future Features

A standardized response layer also provides a solid foundation for future Escrow integration features.

Upcoming lessons may introduce:

  • live transaction creation,
  • transaction updates,
  • webhook processing,
  • provider synchronization,
  • enhanced diagnostics,
  • detailed error reporting.

Having one centralized response format makes these enhancements considerably easier to implement.


Expected Outcome

After completing this lesson, the Escrow API client will return every success and failure through a consistent response mechanism.

The external behavior of the client will remain unchanged, but the internal implementation will be significantly cleaner, reducing duplicated code while improving maintainability and readability.


Conclusion

Good software architecture is often about removing repetition rather than adding new functionality.

By centralizing response handling, we’re making the Escrow API client simpler, more consistent, and easier to extend. This refactoring builds upon the improvements introduced in the previous lesson and prepares the client for the increasingly sophisticated payment features that will follow.

In the next lesson, we’ll implement this refactoring by introducing standardized success and error response helpers and updating the Escrow API client to use them throughout.

https://github.com/SplendidDigital/flipnzee-auctions/releases/tag/lesson-129-stable

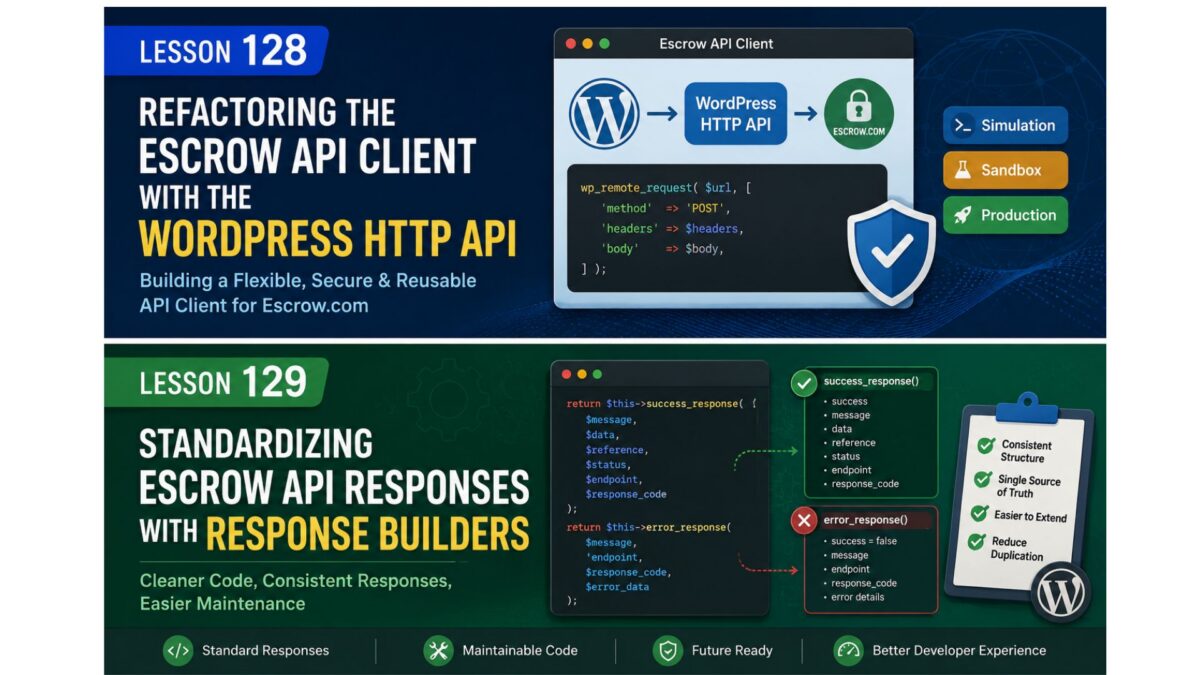
Lesson 129 – Standardizing Escrow API Responses with Response Builders


Objective

Refactor the Escrow API client to eliminate duplicated response arrays by introducing reusable response builder methods.

Instead of manually constructing arrays in every public method, the client will centralize response creation through dedicated helper methods.


Why this refactoring?

After Lesson 128, every public method returns a structure similar to:

array(
    'success'      => true,
    'message'      => '',
    'data'         => array(),
    'reference'    => '',
    'status'       => '',
    'endpoint'     => '',
    'response_code'=> 200,
);

This structure is repeated throughout the class.

Although functional, it introduces unnecessary duplication and increases maintenance effort.


Goals

By the end of this lesson we will:

  • Remove duplicated response arrays.
  • Introduce reusable helper methods.
  • Standardize success responses.
  • Standardize error responses.
  • Improve readability.
  • Reduce future maintenance.

New helper methods

Introduce two new private methods.

success_response()

Responsible for constructing successful API responses.

Example responsibilities:

  • success flag
  • message
  • data
  • reference
  • status
  • endpoint
  • response code

error_response()

Responsible for constructing error responses.

Example responsibilities:

  • success = false
  • error message
  • endpoint
  • response code
  • optional error payload

Refactoring send_request()

Instead of manually returning arrays such as:

return array(
    'success' => false,
    ...
);

the method becomes

return $this->error_response(
    ...
);

Likewise,

return $this->success_response(
    ...
);

Benefits

This provides several advantages.

Single source of truth

Every response follows exactly the same structure.


Easier maintenance

If we later decide to add:

provider
timestamp
request_id
duration

only two helper methods require updating.


Cleaner code

Large repetitive array blocks disappear.

The public methods become easier to understand because they focus on business logic instead of formatting arrays.


Preparing for future lessons

Lesson 129 also prepares the client for future functionality.

Upcoming lessons will introduce:

  • Provider synchronization
  • Escrow transaction lifecycle
  • Webhook handling
  • Audit logging
  • Retry mechanisms

Having standardized response builders greatly simplifies those additions.


Expected outcome

After completing Lesson 129:

  • Every public API method returns standardized responses.
  • Response formatting exists in one place.
  • The Escrow client becomes smaller, cleaner, and easier to extend.

Implementation roadmap

We will:

  1. Create success_response().
  2. Create error_response().
  3. Refactor send_request().
  4. Refactor simulation responses.
  5. Refactor all public API methods.
  6. Verify backward compatibility.

I think this is a natural continuation of Lesson 128. Lesson 128 established how the client communicates with external services; Lesson 129 refines how those communications are represented internally, making the codebase more maintainable before moving on to real Escrow transaction payloads and synchronization.

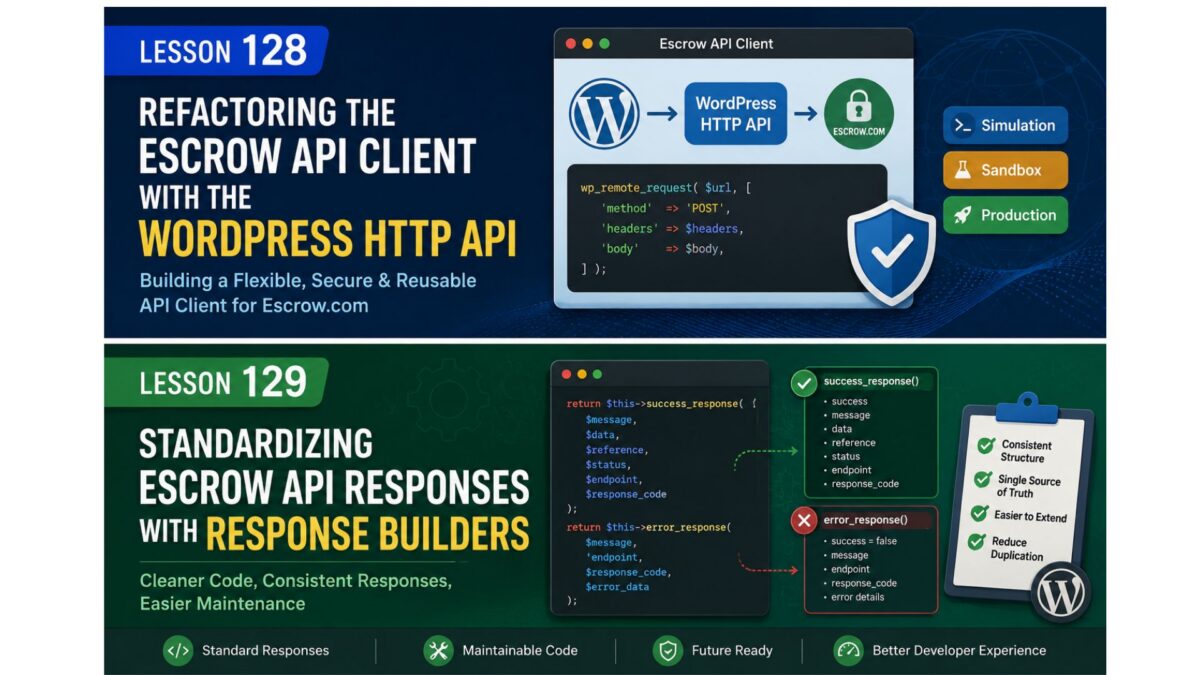
Lesson 128 – Refactoring the Escrow API Client with the WordPress HTTP API

As Flipnzee Auctions continues to evolve from a learning project into a production-ready WordPress plugin, it’s important to periodically pause feature development and improve the underlying architecture.

Our current Escrow API client has served its purpose well by simulating API interactions, allowing us to build and test the payment workflow without relying on external services. However, before integrating with the real Escrow.com API, the client needs to be redesigned into a reusable, maintainable networking component.

In this lesson, we’ll plan that refactoring.


Where We Stand

The current Escrow API client already provides:

  • Simulation mode for development
  • Basic transaction creation methods
  • Transaction status retrieval
  • Connection testing
  • Integration with the Escrow settings page

While functional, much of the networking logic is still tightly coupled to individual methods.

This makes future enhancements more difficult.


Current Limitations

Some of the issues with the existing implementation include:

  • API logic duplicated across multiple methods.
  • No centralized HTTP request handler.
  • Environment handling mixed with business logic.
  • Authentication generated in several places.
  • Difficult to extend for future API endpoints.
  • Response handling not fully standardized.

None of these issues prevent the plugin from working today, but addressing them now will make future development significantly easier.


Objectives of Lesson 128

The primary goal is to transform the Escrow API client into a reusable HTTP client while keeping its public interface compatible with the rest of the plugin.

By the end of this refactoring we want:

  • A cleaner architecture.
  • Better separation of responsibilities.
  • Improved maintainability.
  • Easier testing.
  • Simpler future integration with Escrow.com.

Architectural Changes

Instead of allowing every public method to perform its own networking, we’ll introduce a dedicated request layer.

The new architecture will look like this:

Public API Methods
        │
        ▼
send_request()
        │
        ▼
WordPress HTTP API
        │
        ▼
Escrow REST API

Every network request will pass through a single reusable method.


Environment Support

The refactored client will continue supporting three operating modes:

  • Simulation
  • Sandbox
  • Production

Simulation mode will remain an important development tool, allowing contributors to work on the plugin without requiring live Escrow credentials.


Authentication

Authentication will also be centralized.

Rather than constructing credentials inside individual methods, the client will generate HTTP Basic Authentication headers automatically using the settings saved within the plugin.

This keeps credential handling consistent throughout the class.


WordPress HTTP API

Instead of custom request logic, all communication will use the WordPress HTTP API.

This provides several advantages:

  • Better compatibility with WordPress hosting environments.
  • SSL handling managed by WordPress.
  • Consistent error handling.
  • Proxy support.
  • Easier debugging.

Using native WordPress APIs also keeps the plugin aligned with WordPress development best practices.


Standardized Responses

Another important objective is to ensure every public method returns a predictable structure.

Whether the request succeeds or fails, callers should receive a consistent response containing information such as:

  • Success status
  • Message
  • Provider reference
  • Transaction status
  • Response data
  • Endpoint
  • HTTP response code

This simplifies error handling throughout the rest of the plugin.


Preparing for Future Lessons

This refactoring is not about adding new user-facing features.

Instead, it creates the technical foundation for upcoming work, including:

  • Real Escrow transaction creation
  • Transaction updates
  • Provider synchronization
  • Improved error reporting
  • Webhook support
  • Production deployment

Completing this work now will make those lessons significantly cleaner.


Expected Outcome

After Lesson 128, the Escrow API client will become a reusable networking component rather than a simple simulation helper.

The rest of the plugin will continue using the same public methods, but internally those methods will rely on a much cleaner architecture built around the WordPress HTTP API.


Conclusion

Before integrating with a live payment provider, it’s worth investing time in improving the underlying design.

Refactoring the Escrow API client now will reduce technical debt, improve code quality, and establish a solid networking layer that can support future payment functionality without requiring major architectural changes.

In the next lesson, we’ll implement this new design by introducing a centralized HTTP request handler and refactoring the Escrow API client to use the WordPress HTTP API throughout.

Lesson 128: Refactoring the Escrow API Client with the WordPress HTTP API

In the previous lessons, the Escrow provider relied on a simulated API client. Although this allowed us to build and test the payment workflow without contacting external services, the implementation was tightly coupled to simulation logic and wasn’t ready for real API communication.

In this lesson, we’ll redesign the Escrow API client into a reusable networking component built on top of the WordPress HTTP API. Rather than focusing on Escrow.com specifically, the goal is to establish a clean architecture that can communicate with any REST API while keeping the rest of the plugin independent of transport details.


Why Refactor?

As the plugin grows, responsibilities should become more clearly separated.

Previously, the API client:

  • Simulated responses directly inside public methods.
  • Mixed environment detection with business logic.
  • Had no reusable HTTP layer.
  • Was difficult to extend for production integration.

Instead, we want a client that:

  • Supports multiple environments.
  • Centralizes HTTP communication.
  • Produces consistent response structures.
  • Is easy to test and maintain.

Design Goals

By the end of this lesson, the client should:

  • Support Simulation, Sandbox, and Production modes.
  • Use the WordPress HTTP API (wp_remote_request()).
  • Centralize networking in a reusable request method.
  • Generate HTTP Basic Authentication headers.
  • Return standardized responses.
  • Preserve backwards compatibility with existing provider classes.

Environment-Based Configuration

Instead of relying on a simple boolean flag, the client now loads its configuration directly from the plugin settings.

This allows the same class to operate in different environments without requiring code changes.

Supported environments include:

  • Simulation
  • Sandbox
  • Production

Simulation mode continues to return fake responses so development can proceed safely without contacting Escrow.com.


Centralizing HTTP Requests

One of the biggest improvements is introducing a dedicated request handler.

Rather than each public method performing its own networking, all requests now flow through a single internal method responsible for:

  • Building request URLs
  • Creating headers
  • Encoding JSON payloads
  • Calling the WordPress HTTP API
  • Handling transport errors
  • Decoding JSON responses
  • Returning normalized data

This dramatically reduces duplicated code throughout the client.


Authentication

Authentication is now generated automatically from the saved Escrow settings.

Depending on the selected environment, the client retrieves the appropriate credentials and builds a standard HTTP Basic Authentication header before every request.

This keeps authentication logic in one place while allowing the rest of the plugin to remain unaware of implementation details.


Consistent Responses

Another important improvement is response normalization.

Regardless of whether the client is operating in Simulation, Sandbox, or Production, every public method returns a consistent structure containing information such as:

  • Success status
  • Message
  • Provider reference
  • Transaction status
  • Response data
  • Endpoint information
  • HTTP response code

Having a predictable response format greatly simplifies error handling elsewhere in the plugin.


Simulation Mode

Simulation mode remains an important part of the architecture.

Instead of bypassing the client entirely, simulation requests travel through the same workflow before returning realistic mock responses.

This allows the rest of the plugin to be developed and tested without requiring valid Escrow credentials or network connectivity.


WordPress HTTP API

The client now communicates through the WordPress HTTP API instead of custom networking code.

Using the WordPress HTTP API provides several benefits:

  • WordPress-managed SSL verification
  • Proxy support
  • Better compatibility across hosting environments
  • Consistent error handling
  • Easier future maintenance

It also aligns the plugin with WordPress development best practices.


Logging

Debug logging has been improved to assist development.

When enabled, the client records useful information during requests without exposing sensitive authentication details.

This makes troubleshooting significantly easier while keeping production environments clean when debugging is disabled.


Benefits of the Refactoring

Although the plugin’s visible behavior changes very little, the internal architecture improves substantially.

The Escrow client is now:

  • More modular
  • Easier to understand
  • Easier to extend
  • More reusable
  • Better aligned with WordPress Coding Standards

Most importantly, future lessons can focus entirely on Escrow transaction payloads and provider synchronization without needing to revisit the networking layer.


What We Learned

In this lesson we learned how to:

  • Refactor an API client without changing its public interface.
  • Separate networking concerns from business logic.
  • Use the WordPress HTTP API for REST communication.
  • Support multiple runtime environments.
  • Normalize API responses.
  • Build a maintainable foundation for future payment provider integrations.

Conclusion

Lesson 128 marks an important architectural milestone for Flipnzee Auctions. The Escrow API client has evolved from a simple simulation helper into a reusable networking component capable of supporting real-world API integrations.

While transaction creation and synchronization will continue to evolve in upcoming lessons, the underlying transport layer is now in place. This separation of concerns makes the plugin easier to maintain, easier to test, and better prepared for production use.

In the next lesson, we’ll build on this foundation by improving how Escrow responses are processed and preparing the plugin for real transaction lifecycle management.

https://github.com/SplendidDigital/flipnzee-auctions/releases/tag/lesson-128-stable